Threat Advisories

BIG-IP Integrity Vulnerability Threat Report
CVE-2025-58424

I. Introduction

Application Delivery Controllers (ADCs) are essential to modern networks because they optimize, secure, and manage client-server traffic. F5’s BIG-IP, a critical Application Delivery Controller used across enterprises and government networks, plays a key role in traffic management, SSL/TLS termination, and application delivery. [1]

On October 15, 2025, CVE-2025-58424 was discovered, describing a vulnerability affecting F5’s BIG-IP systems where undisclosed traffic can cause data corruption and unauthorized data modification in protocols that lack message integrity protection. The vulnerability currently affects several versions and configurations of BIG-IP products [2] and has been linked to the BRICKSTORM malware, which is used by state-sponsored actors. Although rated Medium (CVSS v3.1 score 4.5) by the National Vulnerability Database (NVD) [6], the potential for exploitation across critical infrastructure makes immediate patching a priority.

No public reports of active in-the-wild exploitation as of October 28, 2025. However, it is part of a broader set of F5 BIG-IP vulnerabilities disclosed amid a nation-state breach of F5’s internal networks (detected on August 9, 2025) [6], where source code and undisclosed vulnerable details were stolen. This raises concerns for potential zero-day exploits by the threat actor.

Following the public disclosure, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued an Emergency Directive (ED 26-01) for federal agencies. [8] The directive required agencies to apply F5 patches, inventory F5 products, and restrict management interface access. CISA warned that the breach presents an “imminent threat” to federal networks.

This advisory provides a consolidated overview of what CVE-2025-58424 is, where it is targeted towards, affected BIG-IP modules, associated MITRE ATT&CK techniques, as well as recommended mitigations. It serves to help readers understand the technical scope and protections to maintain data integrity and network resilience.

II. Target

CVE-2025-58424 affects the BIG-IP data plane, which is responsible for nearly all runtime network traffic processing, including load balanced traffic by Traffic Management Microkernel (TMM). As a result, any organization running affected F5 BIG-IP products or services that rely on TMM is potentially vulnerable to CVE-2025-58424. These products and services sit at the network edge and handle large volumes of client-server traffic, making successful exploitation extremely dangerous and affecting a wide range of industries [4], including:

  • Enterprise & Cloud Service Providers
  • Financial Services
  • Government & Public Sectors
  • Healthcare
  • Telecommunications
  • Retail & E-commerce

Affected BIG-IP Modules:

The following table lists the BIG-IP modules affected by CVE-2025-58424, as identified in Recorded Future [6], a leading cyber-threat intelligence and vulnerability tracking platform, along with their corresponding function category:

Table 1. BIG-IP Modules Impacted by CVE-2025-58424 and their Functional Classification

III. Tactics and Techniques

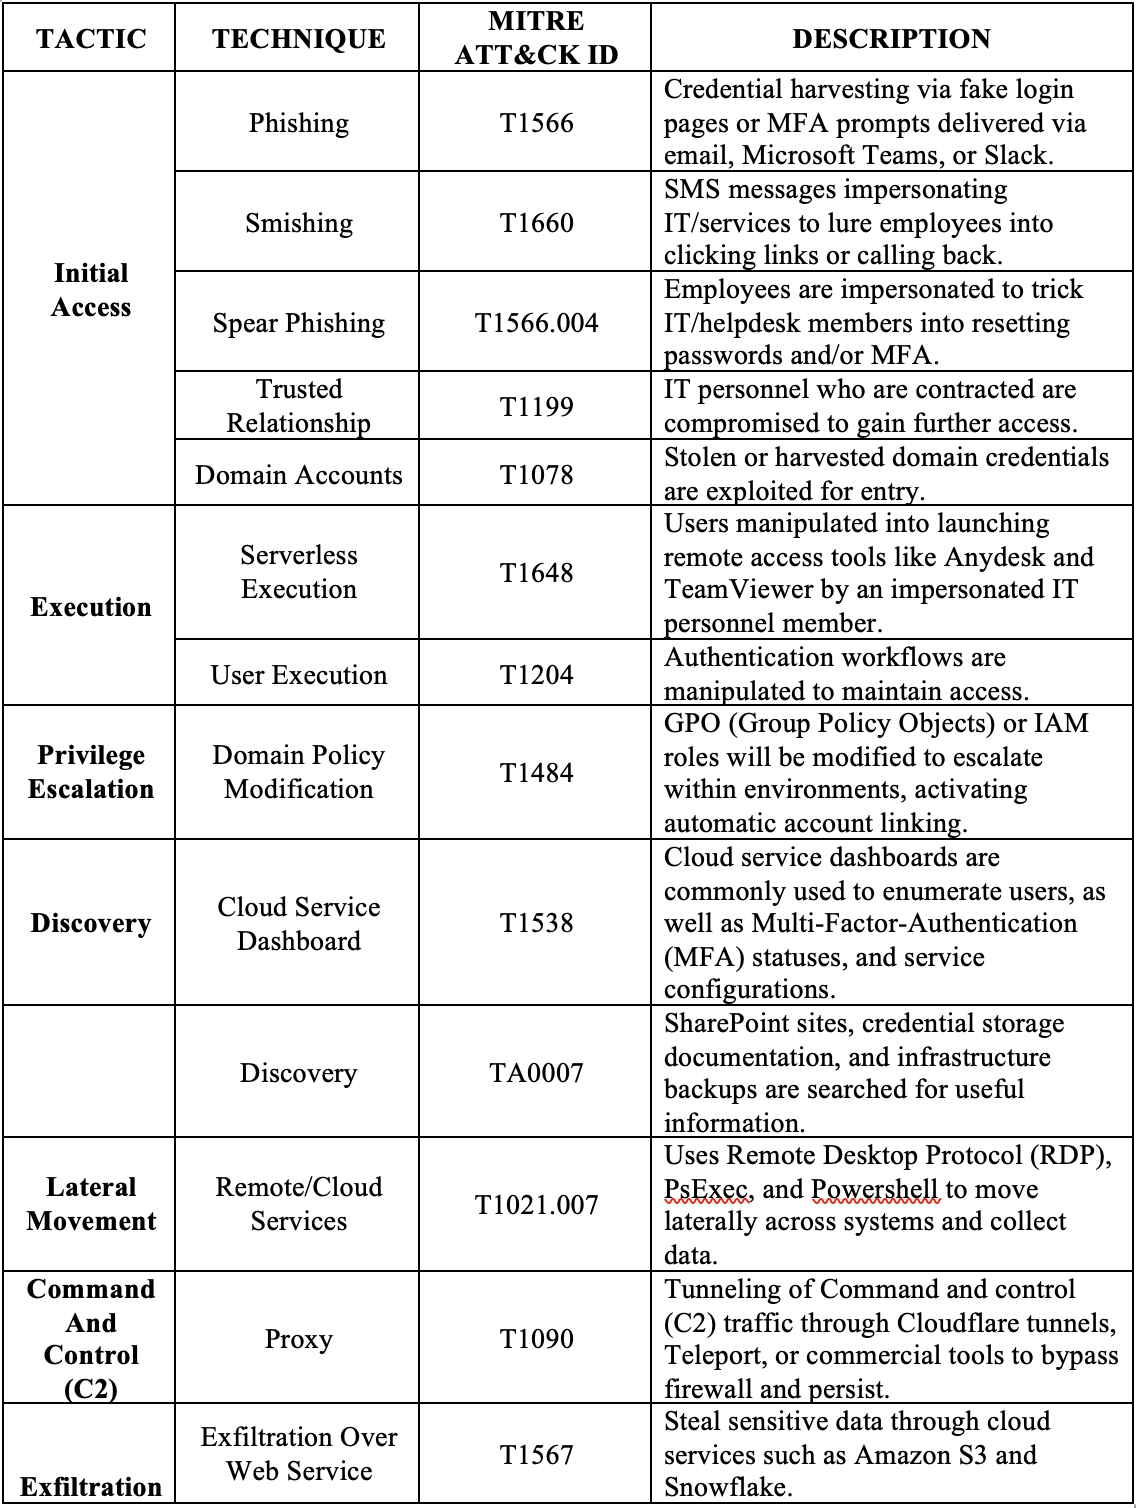
The following table maps out MITRE ATT&CK Techniques Associated with CVE-2025-58424:

Table 2. MITRE ATT&CK Techniques Associated with CVE-2025-58424

IV. Adversary Tools and Services

Although a specific threat actor has not been linked to the F5 breach, public reporting from Google Cloud Mandiant (Mandiant is Google Cloud’s threat intelligence sector that conducts research on advanced persistent threat APT activity and state sponsored cyber activity) suggests that this vulnerability may be of the works of UNC5221, a Chinese threat actor that targets network and edge devices [7]. Attackers using CVE-2025-58424 resemble UNC5221 who have conducted previous campaigns; however, it does not prove that they are the same actor. It only indicated that comparable techniques and similar tools are deployed, which is crucial to monitor in case the same malware or infrastructure recurs in the future.

The primary malware family linked to this vulnerability is BRICKSTORM, a backdoor that allows attackers to gain sustained remote access and command over compromised systems. Due to its cross-platform capabilities, BRICKSTORM can be used on Windows, Linux, and BSD (Berkley Software Distribution), which enables attackers to infiltrate a variety of network environments [7]. In past campaigns, UNC5221 has been observed to have persistence for more than a year (roughly 393 days), showing that they prioritize data collection and being hidden over big attacks that quickly cease access [7].

To stay hidden, this group uses cloud services like Cloudflare Workers and Heroku as part of their command-and-control (C2) blueprint to perform cloud-fronting. Could-fronting is a technique that makes malicious traffic appear to be from reliable businesses. Additionally, they employ DNS-over-HTTPS (DoH), which encrypts network communication to make it difficult for defenders to identify anomalies. After entering the system, this group advances into virtualized environments such as VMware, vCenter, and ESXi, which are frequently found in data centers [7]. This allows them to increase their level of control and remain undetected, even in the event that one machine is isolated or patched.

Recorded Future also discovered that CVE-2025-58424 appears in legitimate penetration testing tools like Tenable Nessus plugin #270590, as well as other tools like the DDoS Toolkit and generic Backdoor malware [6]. This demonstrates that both attackers and defenders are actively using this vulnerability: Adversaries are looking for unpatched targets, and defenders are using it for testing and securing systems.

Altogether, these results demonstrate that CVE-2025-58424 lies in a hybrid threat space that can be exploited by both independent and state-sponsored threat actors. Despite the lack of confirmation regarding who is responsible for F5’s BIG-IP modules, the similarity in tactics and techniques points to a larger campaign approach that emphasizes data manipulation, stealth, and continuous persistence.

V. Indicators of Compromise (IOCs) and Detection Indicators

There are currently no verified Indicators of Compromise (IOCs) available for CVE-2025-58424 as of this advisory. Being that this is a possible early warning sign of exploitation, security teams should keep an eye out for anomalies in outgoing connections to cloud-hosted command-and-control (C2) services and encrypted DNS traffic.

The following table rounds up observable behaviors and network patterns connected to the exploitation activity linked to CVE-2025-58424. Until confirmed IOCs are released, these indicators serve to assist analysts in searching for related activity:

Table 3. Detection and Monitoring Indicators for CVE-2025-58424

VI. Recommendations

CVE-2025-58424 allows attackers to infiltrate and modify data within active TCP sessions that use protocols lacking encryption or message integrity protection, such as those without TLS. The issue stems from predictable identifiers in TMM, that is, the Traffic Management Microkernel, a core component of F5 Networks, which can be leveraged to inject malicious data into the data plane. To mitigate these threats, organizations should implement the following course of action:

  1. Upgrade BIG-IP

F5 have introduced patched versions for affected modules. Organizations using affected models should upgrade to patched versions (15.1.10.8+, 16.1.6+, or 17.5.0+) for optimum security and performance.

For additional guidance:

Navigate to F5’s official website to learn more about common issues and best practices when upgrading BIG-IP systems: https://my.f5.com/manage/s/article/K000157079

  1. Turn on the TCP Injection Protection Setting

Administrators can enable the ‘tm.tcpstopblindinjection’ database variable via the Traffic Management Shell (TMSH) to add an extra layer of protection and serve as temporary mitigation until the patch is applied.

a. Log in to the TMOS Shell (tmsh) with the following command from the Advanced Shell (bash):

Tmsh

b. Enter the following command to enable the ‘tm.tcpstopblindinjection’ database variable:

modify /sys db tm.tcpstopblindinjection value enable

c. Verify the change with the following command:

list /sys db tm.tcpstopblindinjection

To limit exposure, it is recommended to restrict management and self-IP access to trusted networks and enforce TLS across all traffic in addition to patching systems. 8 of 9

Security analysts should maintain increased monitoring of network traffic and logs for unusual TCP behavior, injection attempts, or sequence number anomalies while systems are in the process of being patched. The CVSS score is rated moderate, but the potential for unauthorized data manipulation within live network segments makes this a serious threat that requires immediate attention and remediation.

Table 4. Summary of Affected Products & Fixed Versions
Note: Refer to Table 1 in Section II (Targets) for a complete list of affected BIG-IP modules.

VII. References

[1] F5 Networks. (2025, October). Security Advisory K000156572: BIG-IP Software Vulnerabilities Quarterly Notification | MyF5. https://my.f5.com/manage/s/article/K000156572

[2] National Vulnerability Database (NVD). (2025, October 15). CVE-2025-58424: F5 BIG-IP Traffic Management Microkernel Data Corruption Vulnerability | National Institute of Standards and Technology (NIST). https://nvd.nist.gov/vuln/detail/CVE-2025-58424

[3] F5 Networks. (2025, October 15). Security Advisory K000151297: BIG-IP System Software Security Update for CVE-2025-58424 | MyF5. https://my.f5.com/manage/s/article/K000151297

[4] F5 Networks. (2025, October). Security Advisory K44525501: CVE-2025-58424 BIG-IP Data Plane Vulnerability Overview | MyF5. https://my.f5.com/manage/s/article/K44525501

[5] F5 Networks. (2025, October). Security Advisory K000157079: Upgrading BIG-IP Systems – Best Practices and Mitigation Guidance | MyF5. https://my.f5.com/manage/s/article/K000157079

[6] Recorded Future Insikt Group (2025, October 23). Vulnerability Enrichment: CVE-2025-58424. Recorded Future. https://app.recordedfuture.com/portal/analyst-note/doc:_b2QRX https://cloud.google.com/blog/topics/threat-intelligence/brickstorm-espionage-campaign

[7] Yoder, S., Wolfram, J., Pearson, A., Bienstock, D., Madeley, J., Murchie, J., Slaybaugh, B., Lin, M., Carstairs, G., & Larsen, A. (2025, September 24). Another BRICKSTORM: Stealthy backdoor enabling espionage into tech and legal sectors. Google Cloud Blog. https://cloud.google.com/blog/topics/threat-intelligence/brickstorm-espionage-campaign

[8] Lakshmanan, R. (2025, October 15). F5 breach exposes BIG-IP source code — Nation-state hackers behind massive intrusion. The Hacker News. https://thehackernews.com/2025/10/f5-breach-exposes-big-ip-source-code.html

Threat Advisory created by The Cyber Florida Security Operations Center. Contributing Security Analysts: Taylor Alvarez, Isaiah Johnson, Eduarda Koop, and Waratchaya Luangphairin (June)
BIG-IP Integrity Vulnerability Threat Report2025-11-07T13:24:56-05:00

Scattered Spider Threat Report

I. Introduction

Scattered Spider is a large and loosely affiliated cybercrime group also referred to as UNC3944 or Octo Tempest. This group is made up of teens and young adults who primarily target companies in the U.S. and U.K. for financial gain (CISA, 2025).

Their attacks are heavily reliant on social engineering. Common tactics include bombarding employees with repeated MFA prompts (“push bombing”), hijacking phone numbers through SIM-swap attacks, and impersonating IT help desk staff to steal credentials. Once inside, they use “everyday” administrative tools and legitimate remote access applications to move quietly through networks, steal sensitive data, and in many cases deploy ransomware such as DragonForce [1, 2]. Scattered Spider is a serious concern because they adapt quickly, move across multiple industries, and combine human manipulation with technical persistence. [2, 7]

In today’s fast-paced technological and cybersecurity environment, staying ahead of the game is critical, and members of the Scattered Spider understand this well. They take advantage of the newest technologies, quickly identifying vulnerable areas and exploiting them for attack. For this reason, they have gained reputation as one of the most dangerous threat groups active today.

This report will outline who they target, the tactics they use, indicators of compromise, and how different roles can defend against them.

II. Target

Scattered Spider’s targets span across multiple industries, with the most recent being retail, insurance companies, and aviation. These incidents have impacted many countries worldwide and are most heavily hit in the U.S. and U.K. They go after large companies exploiting help desks and compromising third-party vendors such as customer support platforms, IT contractors, or cloud services. The following examples highlight major attacks between April and July 2025.

  • April 2025
    • Marks and Spencer (Retail, U.K.) – Struck by a ransomware attack that disrupted operations, cut into sales, and exposed customer and employee data. Attackers gained access through social engineering that targeted IT help desks, a tactic characteristic of Scattered Spider [3].
    • Co-op (Retail, U.K.) – Experienced ransomware attacks causing data loss and service outages, negatively affecting company revenue and stock. Investigators revealed that access was granted through the impersonation of support staff and later passed to a ransomware-as-a-service (RaaS) operator, methods closely matching Scattered Spider’s standard techniques [4].
  • May 2025
    • Victoria’s Secret (Retail, U.S.) – Forced to shut down their website and in-store services following a security breach that was part of a wider campaign targeting retail [5].
    • Adidas (Retail, Germany, global) – Confirmed theft of company and customer contact information through a third-party customer service provider [6].
  • June 2025
    • AFLAC (Insurance, U.S.) – Confirmed a data breach with Scattered Spider’s use of social engineering suspected for initial access.
    • Philadelphia Indemnity Insurance (Insurance, U.S.) – Suffered a data breach linked to Scattered Spider’s use of Multi-Factor-Authentication (MFA) fatigue attacks.
    • WestJet (Aviation, Canada) – Data centers breached along with their Microsoft Cloud environment. Scattered Spider gained their initial access through password reset on an employee account and using MFA to gain further access.
    • Hawaiian Airlines (Aviation, U.S.) – Believed to have also been attacked by Scattered Spider, although investigations are ongoing and see similarities in tactics to other airline attacks.
  • July 2025
    • Qantas (Aviation, Australia) – Suffered significant data breach through a third-party customer service platform affecting nearly 6 million customers. Members of the Scattered Spider are believed to be responsible through targeting an IT call center.
    • Azpiral (Loyalty Program Provider, U.K.) – Loyalty program provider for Co-op UK, disclosed a cyberattack extending impact beyond the retail company itself [7].

III. Tactics and Techniques

Scattered Spider incorporates a wide range of Tactics, Techniques, and Procedures (TTPs) to get what they want. They consistently rely on social engineering, most commonly impersonation of IT or Helpdesk personnel to deceive employees into revealing credentials, approving MFA prompts, or granting remote access.

The following list shows their tactics and techniques, along with the corresponding MITRE ATT&CK technique IDs.

IV. Adversary Tools and Services

Scattered Spider relies on social engineering and trusted IT tools rather than custom malware. This helps them stay undiscovered in corporate environments [4].

Based on the recently published reports by CISA (2025) and CrowdStrike (2025), they use the following tools and services to maintain their persistence in the compromised systems:

  1. Remote Access Tools: AnyDesk, TeamViewer, Teleport.sh, and ScreenConnect provide persistent remote connectivity by tunneling over the internet [1].
  2. Cloudflare Tunnels: Cloudflare’s trycloudflare creates encrypted tunnels that bypass company firewalls and VPNs without raising suspicion. [9].
  3. Communication Platforms: Slack, Microsoft Teams and even SMS platforms would be exploited for social engineering, impersonating IT staff and targeting privileged users [9].
  4. Cloud Storage and Databases: Mega.nz, and Amazon S3, and Snowflake are mishandled for large-scale data exfiltration. Thousands of rapid queries would be used to pull out huge amounts of data in a very short time [9].
  5. Living off the Land Tools: PsExec, Powershell and Remote Desktop Protocol (RDP) allows for stealthy command execution, credential theft, and lateral movement disguised as routine I activity [9, 10].
  6. Malware and Ransomware (less common): AveMaria/WareZone (RAT), Racoon and Vidar (stealers), and ALPHV/BlackCat or DragonForce (ransomware) are deployed occasionally for persistence, theft, and extortion [1, 12].

V. Indicators of Compromise (IOCs)

Because Scattered Spider is known for blending in with legitimate user activity, this makes spotting them challenging. To stay ahead of them, defenders should look for subtle anomalies that give away their presence rather than just the tools themselves [11]. These clues, when pieced together, can help identify an attack even before major damage is done.

1. Impersonation Domains: Fake login/helpdesk sites. These domains typically impersonate corporate login or IT helpdesk pages, making them appear trustworthy to targets.

  • In the past they have used: [1]
    • targetsname-sso[.]com,
    • targetsname-servicedesk[.]com,
    • targetsname-okta[.]com,
    • targetsname-helpdesk[.]com,
    • oktalogin-targetcompany[.]com

2. Remote Access Abuse: Unexpected installation of remote access tools like AnyDesk, TeamViewer, Teleport.sh, and ScreenConnect (mentioned above) or unusual connections to unknown domains.

3. Tunneling Traffic: Repeated connections to trycloudflare domains that bypass VPN/firewalls.

4. Abnormal Data Exfiltration Patterns: Bursts of SQL queries executed against databases, large uploads to Mega.nz or Amazon S3 buckets outside of normal workflow [8], or high-volume outbound traffic from accounts or servers that don’t usually transfer large datasets.

5. Credential and Privilege Abuse: Repeated failed login attempts followed by successful access from a new or foreign IPs, unexpected privilege escalations or password resets, and MFA bypass attempts via helpdesk calls (vishing) or SIM swaps [13].

VI. Recommendations

Scattered Spider has impacted a wide range of individuals within targeted organizations by exploiting both human behavior and weaknesses in cloud identity systems. Their tactics allow them to compromise accounts across all levels of a company. Because their attacks touch so many different roles, a one-size-fits-all approach to mitigation would be insufficient.

This report breaks down mitigation strategies by role group, focusing on the four most frequently targeted groups: IT Support and Help Desk Personnel, Identity & Access Administrators, Executives & High-Privilege Users, and Standard Users across the Organization. Each section highlights who these groups are, how they are attacked, and what can be done to reduce the exposure to the attack, boosting resilience to a group whose playbook is to exfiltrate victims’ data and extort them for financial gain.

1. IT Support & Help Desk Personnel: Front-liners responsible for password resets, multi-factor authentication setup/resets, as well as employee account recovery. Scattered Spider targets this group the most by frequently impersonating employees calling IT support and Help desk personnel during after-hours (A time when not many people are around to verify legitimacy) requesting an “authentication reset” to gain remote access on that employee’s device.

How to Defend:

    • Be trained in detecting social engineering, especially during after-hours or peak times when there are multiple requests in short windows.’
    • Create a process that can be implemented for out of band authorization, meaning that if an employee calls saying they have lost their password and phone, be able to differentiate between a legitimate employee calling and a threat actor, like Scattered Spider, calling in to gain initial access.
    • Log and audit all reset/MFA enrollment and reset requests.
    • Block unauthorized Remote Monitoring and Management tools.
    • Use fallback verification channels, such as alternate phone numbers, to confirm identity.

2. Identity & Access Management Administrators: Control who can log into systems and what they can access. IAM Administrators manage passwords, multi-factor authentication, cloud access, and application permissions. They essentially hold the keys to everything. If an attacker compromises an IAM account, they can access multiple systems, escalate privileges to gain even more control, disable protections like MFA, remain hidden longer, exfiltrate sensitive data, or launch larger attacks.

How to Defend:

  • Have strong conditional access policies. Conditional access policies let you restrict logins to known IPs, managed devices, and geofenced locations, as well as specify token lifetimes to be short enough so even if it was stolen it will not work [14].
  • Use stronger multi-factor authentication for admins, such as hardware-based tokens or NFC connections. Hardware tokens are highly resistant to phishing and are not reliant on mobile devices [15].
  • Implement passkeys for employee authentication. Passkeys are cryptographic keys stored directly to a specific device and cannot be linked or synced to other devices [16].
  • Don’t let admin access be “always on.” Give admin access only when necessary, not all the time. (This is also called “just-in-time” access.)
  • Implement allow-listing and block known applications used by Scattered Spider and only allowing specific internal tools used within the company [17].
  • Watch for suspicious activity. Flag whenever someone logs in from a new device or location, or if a login token gets reused.
  • Clean up unused integrations. Disconnect old logins and apps that are no longer used, as they are an easy way to get in.

3. Executives & High-Privilege Users: Individuals with access to extremely valuable data, such as sensitive financial, legal, or insurance information. They are the prime targets for extortion and leveraging attacks due to having broader system privileges across the organization.

Why they are targeted: Offers high-value access with minimal friction. Executives often have direct access to confidential documents; their accounts typically have higher internal trust, and if compromised, could be used to trick others within the organization. Executive accounts are also often over-permissioned and interwoven in multiple high-risk systems, so one compromise can rapidly destruct laterally.

How to Defend:

  • Be phishing savvy.
  • Use hardware-based multi-factor authentication to prevent SIM-swaps and push bombing, a method used to overwhelm a user with repeated multi-factor authentication push notifications in hopes that the user will eventually approve out of annoyance.

4. Standard Users Across the Organization: Everybody else using email, SaaS (Software-As-A-Service, software solutions delivered over the internet on a subscription basis) apps, and cloud tools.

How they are targeted: Phishing, smishing, and multi-factor authentication attacks

How to Defend:

  • Partake in ongoing training with phishing and smishing simulations and report suspicious MFA prompts.
  • Use strong passwords, including no reuse, no hints, and use of password managers.
  • Disable email-based onetime passwords as this can be leveraged to gain onwards authentication.
  • Enable account lockouts after failed login attempts to limit brute-force access.
  • Block unauthorized software, especially remote access or monitoring tools.
  • Update devices and software regularly.
  • Be cautious when uploading or sharing files in cloud platforms like SharePoint, Slack, or email.

VII. References

[1] Scattered spider: Cisa. Cybersecurity and Infrastructure Security Agency CISA. (2025, July 31). https://www.cisa.gov/news-events/cybersecurity-advisories/aa23-320a

[2] Scattered spider. Scattered Spider, Roasted 0ktapus, Octo Tempest, Storm-0875, Group G1015 | MITRE ATT&CK®. (2024, April 4). https://attack.mitre.org/versions/v17/groups/G1015/

[3] Tidy, J. (2025, May 21). M&S and co-op hacks: Scattered spider is focus of police investigation. BBC News. https://www.bbc.com/news/articles/ckgnndrgxv3

[4] Poston, H. (2022, March 21). £300m gone: How scattered spider hit the UK’s biggest retailers. Hack The Box. https://www.hackthebox.com/blog/scattered-spider-insurance-retail-attacks

[5] Silberstein, N. (2025, June 13). Update: May cyber attack expected to cost victoria’s secret $20 million. Retail TouchPoints. https://www.retailtouchpoints.com/topics/security/data-security/victorias-secret-latest-hit-in-growing-swath-of-retail-cyber-attacks

[6] Beek, K. (2025, May 27). Adidas falls victim to third-party Data Breach. https://www.darkreading.com/vulnerabilities-threats/adidas-victim-third-party-data-breach

[7] Scattered spider targets tech companies for help-desk exploitation. ReliaQuest. (2025, June 23). https://reliaquest.com/blog/scattered-spider-cyber-attacks-using-phishing-social-engineering-2025/

[8] Fadilpašić, S. (2025, July 30). FBI, CISA warn of more scattered spider attacks to come. TechRadar. https://www.techradar.com/pro/security/fbi-cisa-warn-of-more-scattered-spider-attacks-to-come

[9] Scattered spider escalates attacks across industries. CrowdStrike. (n.d.). https://www.crowdstrike.com/en-us/blog/crowdstrike-services-observes-scattered-spider-escalate-attacks/

[10] Yasir, S. (2025, July 7). Inside the scattered Spider Attack: How a UK retail giant was breached and what it means for… Medium. https://medium.com/@shaheeryasirofficial/inside-the-scattered-spider-attack-how-a-uk-retail-giant-was-breached-and-what-it-means-for-e3e94a7ce5bf

[11] Richardson, J. (2025, July 29). Scattered spider: The looming shadow over U.S. cybersecurity. Medium. https://medium.com/@the-prototype/scattered-spider-the-looming-shadow-over-u-s-cybersecurity-e8ce141185a5

[12] Tahir. (2025, May 2). Unmasking the scattered Spider Threat actor. Medium. https://medium.com/@tahirbalarabe2/%EF%B8%8Funmasking-the-scattered-spider-threat-actor-6435c2439ed7

[13] Doyle, A., & Langley, M. (2025, June 9). Scattered spider: A web of social engineering – threat actors. Daily Security Review. https://dailysecurityreview.com/resources/threat-actors-resources/scattered-spider-a-web-of-social-engineering/

[14] Shastri, V. (2025, January 15). What is conditional access?. CrowdStrike. https://www.crowdstrike.com/en-us/cybersecurity-101/identity-protection/conditional-access/

[15] Horn, P. (2025, July 11). Passkeys vs Hardware Tokens: Phishing-resistant MFA. Accutive Security – The IAM + Crypto Products and Services Company. https://accutivesecurity.com/guide-to-passkeys-and-hardware-security-tokens-yubikeys/

[16] Passkeys: Passwordless authentication. FIDO Alliance. (2025, July 24). https://fidoalliance.org/passkeys/

[17] What is allowlisting?: Broadcom. Broadcom Inc. (n.d.). https://www.broadcom.com/topics/allowlisting

Threat Advisory created by The Cyber Florida Security Operations Center. Contributing Security Analysts: Waratchaya Luangphairin (June), Taylor Alvarez, Lara Radovanovic, Sneha Lama

To learn more about Cyber Florida visit: www.cyberflorida.org

Scattered Spider Threat Report2025-09-12T13:13:50-04:00

Deepfake Cyber Threats: Understanding the Risks of AI-Powered Fraud and Scams

I. Targeted Entities

Deepfake technologies pose a threat to a wide range of entities, including but not limited to:

  • Individuals / General Public
  • Politicians and Political Processes
  • Celebrities and Public Figures
  • Organizations and Corporations:
    • Senior Executives
    • Financial Sector
  • Government Officials and Agencies

II. Introduction and Key Treat Details

Introduction

Synthetic media generated by Artificial Intelligence (AI), commonly known as deepfakes, are rapidly multiplying and increasing in sophistication. We are currently witnessing a significant surge in deepfake incidents; for instance, there was a 257% rise in recorded incidents from 2023 to 2024, and the rest quarter of 2025 alone surpassed the total incidents of the previous year.

The potential impacts are severe and varied. These include substantial financial losses for organizations and individuals, as seen by the $25 million fraud at Arup, where executives were impersonated via deepfake video. Deepfakes are key in disinformation campaigns that erode public trust and can influence political outcomes, such as through fake calls targeting voters. Furthermore, the technology is used to create non-consensual explicit content and enhance the effectiveness of social engineering attacks.

As outlined in Section I, targets span from the general public and public gures to corporations (particularly in nance) and government entities. Addressing this emerging threat requires a multi-layered strategy. Organizations must implement robust cybersecurity policies, conduct continuous employee awareness training, deploy technical safeguards, and enforce strict verification protocols. Also, individuals need to develop media literacy, enhance personal data security, and be skeptical of certain online information. Ocial bodies, such as the FBI, are increasingly issuing warnings and guidance, indicating a move towards more collaborative defense.

Key Threat Details

Threat Type: The threat involves the malicious use of deepfakes, which are AI-generated synthetic media (audio, video, or images) carefully crafted to impersonate real individuals or fabricate events that never occurred. The primary technology empowering deepfakes is Generative Adversarial Networks (GANs). A GAN consists of two neural networks: a 'generator' that creates the fake content and a 'discriminator' that attempts to distinguish the fake content from authentic examples. Through an iterative, adversarial training process, the generator becomes progressively better at creating realistic fakes that can deceive the discriminator, and ultimately, human perception. This technology is leveraged by increasingly accessible software, with tools like Iperov's DeepFaceLab and FaceSwap, and services like Voice.ai, Mur.ai, and Elevenlabs.io for voice cloning.

Targets

  • Individuals (General Public): Targeted for fraud, non-consensual explicit content, and harassment.
  • Politicians and Political Processes: Disinformation campaigns, impersonation to influence elections, and reputational attacks.
  • Celebrities and Public Figures: Often targeted for non-consensual explicit content, endorsement scams, and reputational damage.
  • Organizations and Corporations:
    • Senior Executives (CEOs, CFOs): Impersonated in financial fraud schemes.
  • Financial Sector: Targeted for large-scale fraud, market manipulation through disinformation, and undermining customer trust.
  • Government Officials and Agencies: Impersonated to obtain sensitive information, spread disinformation, or authorize fraudulent actions.

Impact

If successful, deepfake attacks can lead to:

  • Financial Fraud: Significant monetary losses through impersonation of executives or trusted parties to authorize fraudulent transactions (vishing).
  • Disinformation and Political Destabilization: Manipulation of public opinion, interference in elections, incitement of social unrest, and damage to democratic processes.
  • Reputational Harm: Severe damage to personal or corporate reputations through the creation and dissemination of non-consensual explicit material, defamatory statements, or fabricated incriminating evidence.
  • Social Engineering and Data Breaches: Gaining unauthorized access to sensitive systems or information by impersonating trusted individuals and deceiving employees.
  • Erosion of Trust: Diminished public trust in authentic media, institutions, and digital communication ("liar's dividend").
  • Operational Disruption: Business operations can be disrupted by disinformation campaigns or internal fraud incidents.

Contextual Info

Deepfake technology is accessible to a wide spectrum of malicious actors. This includes individual fraudsters, online harassers, organized criminal enterprises focused on financial gain, and potentially state-sponsored groups deploying deepfakes for complex disinformation campaigns and political interference.

Related Campaigns/Past Activity

The versatility of deepfakes is seen through various high-prole incidents:

  • The $25 million financial fraud at Arup, where attackers used deepfake video and audio to impersonate senior executives in a conference call, compelling an employee to make unauthorized transfers.
  • AI-generated calls impersonating U.S. President Joe Biden, which urged voters in New Hampshire not to participate in the primary election, representing a direct attempt at election interference.
  • The widespread creation and distribution of non-consensual explicit deepfake images of public gures like Taylor Swi, highlighting the potential for severe personal and reputational harm.

MITRE ATT&CK TTPs

T1566 Phishing: Deepfakes, especially audio (voice clones), are used in vishing (voice phishing) campaigns, aligning with sub-techniques like T1566.003 Spearphishing Voice.

T1591.002 Create/Modify Content: Deepfakes inherently involve creating or modifying content to deceive, related to broader information operations or influence campaigns.

IV. Recommendations

For Organizations

Policies:

  • Develop and enforce robust cybersecurity policies that address the risks of deepfake attacks. Integrate deepfake scenarios into incident response plans and conduct regular practice incidents.
  • Establish clear guidelines on the acceptable use of AI and synthetic media tools within the organization.

Awareness/Training:

  • Implement continuous security awareness training for all employees, leadership, and relevant third parties. Training should cover deepfake identification, the psychological tactics used by attackers (e.g., urgency, authority bias), and established reporting procedures.

Technical Safeguards:

Enforce strong Multi-Factor Authentication (MFA) across all systems and users, prioritizing stronger methods for critical access points.

Deploy AI-powered detection tools for high-risk communication channels (e.g., video conferencing, customer service calls).

Adopt a Zero Trust security architecture, assuming no user or device is inherently trustworthy without continuous verification.

Monitor for Virtual Camera Software in Logs: For live deepfake attacks, attackers may use virtual camera software like Open Broadcaster Software (OBS) to feed the manipulated video into the meeting application. If logging is enabled for platforms like Zoom or Microsoft Teams, security teams can review logs for camera device names. The presence of uncommon camera names like 'OBS Virtual Camera' can be a strong indicator of a deepfake attempt, since this software is not typically used by employees for standard meetings.

Verification and Controls:

  • Implement strict verification (e.g., phone call authentication) for any unusual or high-value requests, specifically those involving financial transfers, changes to payment details, or disclosure of sensitive information over digital channels.
    • Implement "master passcodes" or challenge questions for authenticating identities during sensitive communications.
    • Enforce dual approvals for significant decisions/transactions.

Preventative Measures:

  • Minimize the public availability of audiovisual material of executives/employees to limit training data for attackers.
  • Assess organizational susceptibility to deepfake attacks, identifying vulnerable processes and personnel.

For Individuals

Increase Media Literacy and Critical Thinking:

  • Approach online content with healthy skepticism. Question the authenticity of unexpected, sensational, or emotionally manipulative videos, audio messages, or images.
  • Always consider the source of information. Verify claims through multiple reputable sources before accepting them as true.

Recognize Potential Red Flags:

  • Be aware of common visual indicators such as unnatural eye movements, mismatched lighting, a face that flickers when an object passes in front of it, or an unwillingness from the person to show their side prole. For audio, listen for robotic cadence, unnatural pitch, or lack of emotional inection. 17 However, understand that sophisticated deepfakes may not exhibit obvious aws.

Protect Personal Data:

  • Review and tighten privacy settings on all social media accounts to limit public access to personal images, videos, and information.
  • Be mindful of the amount of personal audiovisual data shared online.

Verify and Report:

  • If you receive a suspicious or urgent request, even if it appears to be from a known contact, verify it through a separate, trusted communication channel (e.g., call a known phone number).
  • Report suspected deepfakes immediately to the platform where they are hosted. If the deepfake is being used for malicious purposes (e.g., fraud, harassment, defamation, non-consensual explicit content), report it to law enforcement agencies.

VII. References

Works cited

Deepfake statistics 2025: how frequently are celebrities targeted?, accessed June 7, 2025, hps://surfshark.com/research/study/deepfake-statistics

Cybercrime: Lessons learned from a $25m deepfake attack | World …, accessed June 7, 2025, hps://www.weforum.org/stories/2025/02/deepfake-ai-cybercrime-arup/

Understanding the Hidden Costs of Deepfake Fraud in Finance – Reality Defender, accessed June 7, 2025, hps://www.realitydefender.com/insights/understanding-the-hidden-costs-of-de epfake-fraud-in-nance

Top 5 Cases of AI Deepfake Fraud From 2024 Exposed | Blog – Incode, accessed June 7, 2025, hps://incode.com/blog/top-5-cases-of-ai-deepfake-fraud-from-2024-exposed/

Gauging the AI Threat to Free and Fair Elections | Brennan Center for Justice, accessed June 7, 2025, hps://www.brennancenter.org/our-work/analysis-opinion/gauging-ai-threat-free-and-fair-elections

FBI warns of fake texts, deepfake calls impersonating senior U.S. …, accessed June 7, 2025, hps://cyberscoop.com/i-warns-of-ai-deepfake-phishing-impersonating-government-ocials/

Top 10 Terrifying Deepfake Examples – Arya.ai, accessed June 7, 2025, hps://arya.ai/blog/top-deepfake-incidents

Deepfake threats to companies – KPMG International, accessed June 7, 2025,hps://kpmg.com/xx/en/our-insights/risk-and-regulation/deepfake-threats.html

Cybercrime Trends: Social Engineering via Deepfakes | Lumi Cybersecurity, accessed June 7, 2025,hps://www.lumicyber.com/blog/cybercrime-trends-social-engineering-via-dee pfakes/

Investigation nds social media companies help enable explicit deepfakes with ads for AI tools – CBS News, accessed June 7, 2025, hps://www.cbsnews.com/video/investigation-nds-social-media-companies-he lp-enable-explicit-deepfakes-with-ads-for-ai-tools/

How to Mitigate Deepfake Threats: A Security Awareness Guide – TitanHQ, accessed June 7, 2025, hps://www.titanhq.com/security-awareness-training/guide-mitigate-deepfakes/

Deepfake Defense: Your Shield Against Digital Deceit | McAfee AI Hub, accessed June 7, 2025, hps://www.mcafee.com/ai/news/deepfake-defense-your-8-step-shield-against-digital-deceit/

FBI Warns of Deepfake Messages Impersonating Senior Ocials …, accessed, June 7, 2025, hps://www.securityweek.com/i-warns-of-deepfake-messages-impersonating-senior-ocials/

FBI Alert of Malicious Campaign Impersonating U.S. Ocials Points to the Urgent Need for Identity Verication – BlackCloak | Protect Your Digital Life™, accessed June 7, 2025, hps://blackcloak.io/i-alert-of-malicious-campaign-impersonating-u-s-ocials-points-to-the-urgent-need-for-identity-verication/

AI's Role in Deepfake Countermeasures and Detection Essentials from Tonex, Inc. | NICCS, accessed June 7, 2025, hps://niccs.cisa.gov/training/catalog/tonex/ais-role-deepfake-countermeasures-and-detection-essentials

What is a Deepfake Aack? | CrowdStrike, accessed June 7, 2025, hps://www.crowdstrike.com/en-us/cybersecurity-101/social-engineering/deepfa ke-aack/

Determine Credibility (Evaluating): Deepfakes – Milner Library Guides, accessed June 7, 2025, hps://guides.library.illinoisstate.edu/evaluating/deepfakes

Understanding the Impact of Deepfake Technology – HP.com, accessed June 7, 2025, hps://www.hp.com/hk-en/shop/tech-takes/post/understanding-impact-deepfake-technology

19.Deepfakes: Denition, Types & Key Examples – SentinelOne, accessed June 7, 2025, hps://www.sentinelone.com/cybersecurity-101/cybersecurity/deepfakes/

en.wikipedia.org, accessed June 7, 2025, hps://en.wikipedia.org/wiki/Deepfake#:~:text=While%20the%20act%20of%20cr eating,generative%20adversarial%20networks%20(GANs).

What are deepfakes? – Malwarebytes, accessed June 7, 2025, hps://www.malwarebytes.com/cybersecurity/basics/deepfakes

Complete Guide to Generative Adversarial Network (GAN) – Carmatec, accessed June 7, 2025, hps://www.carmatec.com/blog/complete-guide-to-generative-adversarial-network-gan/

How to Get Started with GANs: A Step-by-Step Tutorial – Draw My Text – Text-to-Image AI Generator, accessed June 7, 2025, hps://drawmytext.com/how-to-get-started-with-gans-a-step-by-step-tutorial/

Detection of AI Deepfake and Fraud in Online Payments Using GAN-Based Models – arXiv, accessed June 7, 2025, hps://arxiv.org/pdf/2501.07033

What is a GAN? – Generative Adversarial Networks Explained – AWS, accessed June 7, 2025, hps://aws.amazon.com/what-is/gan/

Overview of GAN Structure | Machine Learning – Google for Developers,accessed June 7, 2025, hps://developers.google.com/machine-learning/gan/gan_structure

Unlocking the Power of GAN Architecture Diagram: A Comprehensive Guide for Developers, accessed June 7, 2025, hps://www.byteplus.com/en/topic/110690

We Looked at 78 Election Deepfakes. Political Misinformation Is Not an AI Problem., accessed June 7, 2025, hps://knightcolumbia.org/blog/we-looked-at-78-election-deepfakes-political-misinformation-is-not-an-ai-problem

What is a deepfake? – Internet Maers, accessed June 7, 2025, hps://www.internetmaers.org/resources/what-is-a-deepfake/

Don't Be Fooled: 5 Strategies to Defeat Deepfake Fraud – Facia.ai, accessed June 7, 2025, hps://facia.ai/blog/dont-be-fooled-5-strategies-to-defeat-deepfake-fraud/

Top 10 AI Deepfake Detection Tools to Combat Digital Deception in 2025 SOCRadar, accessed June 7, 2025, hps://socradar.io/top-10-ai-deepfake-detection-tools-2025/

How to Spot Deepfakes – Fake News – Dr. Martin Luther King, Jr. Library at San José State University Library, accessed June 7, 2025, hps://library.sjsu.edu/fake-news/deepfakes

Threat Advisory created by The Cyber Florida Security Operations Center. Contributing Security Analysts: Derek Kravetsky

Deepfake Cyber Threats: Understanding the Risks of AI-Powered Fraud and Scams2025-07-02T09:38:08-04:00

Russian GRU Targeting Western Logistics Entities and Technology Companies

I. Targeted Entities

  • Western logistics entities and technology companies involved in transportation and coordination of aid to Ukraine.
  • Defense industry entities
  • Transportation hubs (ports, airports)
  • Maritime sectors
  • Air traffic management systems
  • IT services

II. Introduction

Since early 2022, the Russian General Staff Main Intelligence Directorate (GRU), specifically its 85th Main Special Service Center (85th GTsSS), also identified as APT28, Fancy Bear, Forest Blizzard, and BlueDelta, has been actively conducting cyber espionage operations against Western logistics and technology entities. This ongoing campaign primarily targets entities facilitating foreign assistance to Ukraine, highlighting a strategic effort to monitor, disrupt, or influence the flow of aid to Ukraine.

Attack Details: The GRU unit 26165 has leveraged sophisticated cyber espionage tactics, including credential guessing, spearphishing, exploitation of known vulnerabilities, and abuse of internet-facing infrastructure such as corporate VPNs. Notable vulnerabilities exploited in this campaign include CVE-2023-23397 (Outlook NTLM), CVE-2023-38831 (WinRAR), and several Roundcube vulnerabilities (CVE-2020-12641, CVE-2020-35730, CVE-2021-44026).

Recent analysis highlights the GRU’s use of geopolitical event lures, notably exploiting the Israel-Hamas conflict to deliver the HEADLACE malware, enabling comprehensive network penetration and persistent espionage (Mühr, Zaboeva, & Fasulo, 2025).

III. MITRE ATT&CK Framework

Initial Access:

  • Exploitation of Public-Facing Applications (T1190)
    • Exploited known vulnerabilities in publicly accessible applications such as Microsoft Exchange and corporate VPNs to achieve initial entry.
  • Spearphishing (T1566)
    • Distributed carefully crafted phishing emails using contextually relevant geopolitical lures (e.g., Israel-Hamas conflict) to trick users into executing malicious payloads.
  • Brute Force and Credential Guessing (T1110)
    • Conducted systematic credential guessing and brute force attacks targeting exposed remote services, including RDP and VPN logins.

Execution:

  • Command and Scripting Interpreter (T1059)
    • Command and Scripting Interpreter (T1059) is a highly prevalent execution technique in MITRE ATT&CK that adversaries use to run arbitrary commands, scripts, or binaries on target systems via built in interpreters like PowerShell, cmd.exe, Bash, Python, JavaScript, AppleScript, Visual Basic and more.
  • User Execution (T1204)
    • Deployed malicious attachments and phishing links designed to prompt users into inadvertently executing malicious scripts or payloads.

Persistence:

  • Scheduled Task (T1053)
    • Established scheduled tasks to regularly execute malicious scripts and maintain long-term access.
  • • Shortcut Modification (T1547.009)
  • o Altered desktop shortcuts to point to malicious executables, ensuring persistent and subtle execution during regular user operations.

Privilege Escalation:

  • Abuse of Elevation Control Mechanisms (T1548)
    • Exploited software vulnerabilities, notably CVE-2023-23397, enabling unauthorized elevation of privileges to access sensitive resources.

Credential Access:

  • Credential Dumping (T1003)
    • Harvested credentials through techniques such as memory scraping, registry dumps, and exploitation of NTLM hashes.
  • Exploitation of NTLM Vulnerability (CVE-2023-23397)
    • CVE 2023 23397 is a critical “zero touch” elevation of privilege vulnerability in Microsoft Outlook for Windows that allows attackers to exfiltrate a user’s Net NTLMv2 hash without any user interaction.

Lateral Movement:

  • Remote Desktop Protocol (T1021.001)
    • Employed Remote Desktop Protocol to navigate laterally through compromised networks, enhancing the attacker’s reach and access.
  • Use of tools such as Impacket and PsExec
    • Impacket is a Python-based collection of modules that allows attackers to craft and send network protocol packets, making it particularly useful for exploiting protocols like SMB, RDP, and Kerberos. It’s frequently used to perform pass-the-hash, NTLM relay, and DCSync attacks.
  • PsExec, part of Microsoft Sysinternals, enables remote execution of processes and is commonly used by adversaries to run commands or deploy payloads across a network without needing remote desktop access.

Discovery:

  • Active Directory Enumeration (T1087)
    • Mapped organizational structures by enumerating Active Directory objects to identify high-value targets.
  • Network Service Scanning (T1046)
    • Conducted extensive internal scans post-compromise to locate vulnerable or exploitable network services.

Command and Control:

  • Application Layer Protocol (T1071)
    • Used standard protocols such as HTTP(S) and DNS to blend malicious traffic with legitimate communications, complicating detection efforts.
  • Legitimate Web Services (T1102)
    • Leveraged trusted cloud and hosting services to host command and control infrastructure, reducing suspicion and bypassing traditional network defenses.

Exfiltration:

  • Data Exfiltration via Command and Control Channel (T1041)

Phase Technique Description
Data Prep T1560.001 ZIP compression via PowerShell
Exfiltration Channel T1041 Upload via C2 (SSH or API)
Tools – Impacket, PsExec, Certipy, ADExplorer, SSH
Timing Strategy – Periodic bursts, geo-proximity, stealth scheduling
  • Archive Collected Data (T1560)
    • Compressed and encrypted sensitive data into ZIP files using PowerShell scripts for exfiltration.

IV. Indicators of Compromise (IOCs)

  • IP Addresses observed in brute force activities:
  • 103[.]97[.]203[.]29
  • 109[.]95[.]151[.]207
  • 138[.]199[.]59[.]43
  • 147[.]135[.]209[.]245
  • 162[.]210[.]194[.]2
  • 178[.]235[.]191[.]182
  • 178[.]37[.]97[.]243
  • 185[.]234[.]235[.]69
  • 192[.]162[.]174[.]67
  • 192[.]162[.]174[.]94
  • 194[.]187[.]180[.]20
  • 207[.]244[.]71[.]84
  • 209[.]14[.]71[.]127
  • 212[.]127[.]78[.]170
  • 213[.]134[.]184[.]167
  • 31[.]135[.]199[.]145
  • 31[.]42[.]4[.]138
  • 46[.]112[.]70[.]252
  • 46[.]248[.]185[.]236
  • 64[.]176[.]67[.]117
  • 64[.]176[.]69[.]196
  • 64[.]176[.]70[.]18
  • 64[.]176[.]70[.]238
  • 64[.]176[.]71[.]201
  • 70[.]34[.]242[.]220
  • 70[.]34[.]243[.]226
  • 70[.]34[.]244[.]100
  • 70[.]34[.]245[.]215
  • 70[.]34[.]252[.]168
  • 70[.]34[.]252[.]186
  • 70[.]34[.]252[.]222
  • 70[.]34[.]253[.]13
  • 70[.]34[.]253[.]247
  • 70[.]34[.]254[.]245
  • 79[.]184[.]25[.]198
  • 79[.]185[.]5[.]142
  • 83[.]10[.]46[.]174
  • 83[.]168[.]66[.]145
  • 83[.]168[.]78[.]27
  • 83[.]168[.]78[.]31
  • 83[.]168[.]78[.]55
  • 83[.]23[.]130[.]49
  • 83[.]29[.]138[.]115
  • 89[.]64[.]70[.]69
  • 90[.]156[.]4[.]204
  • 91[.]149[.]202[.]215
  • 91[.]149[.]203[.]73
  • 91[.]149[.]219[.]158
  • 91[.]149[.]219[.]23
  • 91[.]149[.]223[.]130
  • 91[.]149[.]253[.]118
  • 91[.]149[.]253[.]198
  • 91[.]149[.]253[.]204
  • 91[.]149[.]253[.]20
  • 91[.]149[.]254[.]75
  • 91[.]149[.]255[.]122
  • 91[.]149[.]255[.]19
  • 91[.]149[.]255[.]195
  • 91[.]221[.]88[.]76
  • 93[.]105[.]185[.]139
  • 95[.]215[.]76[.]209
  • Outlook CVE Exploitation IOCs

    • md-shoeb@alfathdoor[.]com[.]sa
    • jayam@wizzsolutions[.]com
    • accounts@regencyservice[.]in
    • m.salim@tsc-me[.]com
    • vikram.anand@4ginfosource[.]com
    • mdelafuente@ukwwfze[.]com
    • sarah@cosmicgold469[.]co[.]za
    • franch1.lanka@bplanka[.]com
    • commerical@vanadrink[.]com
    • maint@goldenloaduae[.]com
    • karina@bhpcapital[.]com
    • tv@coastalareabank[.]com
    • ashoke.kumar@hbclife[.]in
    • 213[.]32[.]252[.]221
    • 124[.]168[.]91[.]178
    • 194[.]126[.]178[.]8
    • 159[.]196[.]128[.]120
  • Commonly Used Webmail Providers:
    • portugalmail[.]pt
    • mail-online[.]dk
    • email[.]cz
    • seznam[.]cz
  • Malicious Archive filenames
    • calc.war.zip
      • Hash: 763d47f16a230f7c2d8c135b30535a52d66a1ed 210596333ca1c3890d72e6efc
    • Zeyilname.zip
      • Hash: 22ed5c5cd9c6a351398f1e56efdfb16d52cd33cb4b2062
        37487a03443d3de893
      • Hash: 45e44afeb8b890004fd1cb535978d0754ceaa7129082c
        b72386a80a5532700d1
    • news_week_6.zip
      • Hash: 16bcd167162e4ded71b8c7e9a2587be821d3a752c71fc
        bb2ae64cf1088b62fc0
      • Hash: 5b8c240083cba4442fb6bbb092efd430ce998530cc10f
        d181b3f71845ec190ce
      • Hash: 84638698fdcf2e9e45e7dd560c8d00fb4da6fa32dabaac
        d31b3538d38755dad4
      • Hash: f983d786f4dc2d1793f6b28907c4035c96b6b5c8765ba1
        2dc4510dab0fceabf5
    • war.zip
      • Hash: d37779e16a92da7bd05eae50c64b36e2e2022eb4413
        82be686fda4dbd1800e90
      • Hash: 2ac6735e8e0b23b222161690adf172aec668894d17029
        9e9ff2c54a4ec25b1f4
      • Hash: 8cc664ff412fc80485d0af61fb0617f818d37776e5a06b7
        99f74fe0179b31768
      • Hash: ec64b05307ad52f44fc0bfed6e1ae9a2dc2d093a42a8347f069f3955ce5aaa89
    • SEDE-PV-2023-10-09-1_EN.zip
      • Hash: 8dba6356fdb0e89db9b4dad10fdf3ba37e92ae42d55e7bb8f76b3d10cd7a780c
    • Roadmap.zip
  • Malicious scripts/tools observed:
    • HEADLACE (backdoor)
      • A backdoor used to establish persistent access, execute commands remotely, and maintain stealth communication channels with the attackers.
    • MASEPIE (malware)
      • Custom malware designed for executing remote commands, data theft, and maintaining a persistent foothold within compromised networks.
    • STEELHOOK (credential theft)
      • Specialized malware created to extract and exfiltrate sensitive user credentials, aiding further lateral movement and deeper infiltration.

V. Recommendations

  • Patch Known Vulnerabilities:
    • Regularly update all software and firmware.
    • Conduct continuous vulnerability assessments to identify and mitigate security gaps.
  • Enhance Detection and Monitoring:
    • Deploy endpoint detection and response (EDR) systems.
    • Utilize behavioral analysis tools to detect anomalous activities.
  • Strengthen Authentication Practices:
    • Implement multi-factor authentication (MFA).
    • Regularly audit user permissions and account activities.
  • Network Security:
    • Employ network segmentation.
    • Block unauthorized VPN and proxy services.
  • User Awareness:
    • Conduct regular security training focusing on recognizing phishing and social engineering tactics.
  • Incident Response Preparation:
    • Establish and routinely test incident response protocols to quickly contain and remediate intrusions.

VI. Conclusion

Given the strategic nature of this campaign targeting critical logistical infrastructure, Western logistics and technology entities must maintain heightened vigilance. Employing comprehensive security measures and regular training will be crucial in mitigating the ongoing threat posed by the GRU’s advanced cyber espionage operations.

VII. References

Command and scripting interpreter. Command and Scripting Interpreter, Technique T1059 – Enterprise | MITRE ATT&CK®. (n.d.). https://attack.mitre.org/techniques/T1059/

Exfiltration over C2 channel. Exfiltration Over C2 Channel, Technique T1041 – Enterprise | MITRE ATT&CK®. (n.d.). https://attack.mitre.org/techniques/T1041/

Insikt Group. (2025, April 30). France Ties Russian APT28 to Attacks Targeting French Infrastructure and Institutions. Recorded Future. https://app.recordedfuture.com/portal/research/insikt/doc:5pGMcT?organization=uhash%3A5SiRB4MNDF

Insikt Group. (2024, May 30). GRU’s BlueDelta Targets Key Networks in Europe with Multi-Phase Espionage Campaigns. Recorded Future. https://go.recordedfuture.com/hubfs/reports/CTA-RU-2024-0530.pdf

Lesnewich, G., & Giering, C. (2023, December 5). TA422’s dedicated exploitation loop-the same week after week. Proofpoint. https://www.proofpoint.com/us/blog/threat-insight/ta422s-dedicated-exploitation-loop-same-week-after-week

Martin, A. (2025, May 21). Western intelligence agencies unite to expose Russian hacking campaign against logistics and Tech firms. Cyber Security News | The Record. https://therecord.media/western-intelligence-alert-russia-hackers-logistics-fancy-bear-apt28

Microsoft Incident Response. (2025, June 18). Guidance for investigating attacks using CVE-2023-23397. Microsoft Security Blog. https://www.microsoft.com/en-us/security/blog/2023/03/24/guidance-for-investigating-attacks-using-cve-2023-23397

Mühr, G., Zaboeva, C., & Fasulo, J. (2025, April 17). ITG05 operations leverage Israel-hamas conflict lures to deliver Headlace malware. IBM. https://www.ibm.com/think/x-force/itg05-ops-leverage-israel-hamas-conflict-lures-to-deliver-headlace-malware

Ribeiro, A. (2025, May 25). Russian GRU’s unit 26165 conducts two-year cyber espionage on logistics, Tech firms using IP cameras, supply chains. Industrial Cyber. https://industrialcyber.co/cisa/russian-grus-unit-26165-conducts-two-year-cyber-espionage-on-logistics-tech-firms-using-ip-cameras-supply-chains/

Russian GRU Targeting Western Logistics Entities and Technology Companies. U.S. Department of Defense. (2025, May). https://media.defense.gov/2025/May/21/2003719846/-1/-1/0/CSA_RUSSIAN_GRU_TARGET_LOGISTICS.PDF

Russian GRU targeting western logistics entities and technology companies: CISA. Cybersecurity and Infrastructure Security Agency CISA. (2025, May 21). https://www.cisa.gov/news-events/cybersecurity-advisories/aa25-141a

Threat Advisory created by The Cyber Florida Security Operations Center. Contributing Security Analyst(s): Kevin Wong, Jason Doan

Russian GRU Targeting Western Logistics Entities and Technology Companies2025-06-27T09:30:56-04:00

Gorilla Bot Malware Analysis

I. Targeted Entities

  • Financial Institutions
  • E-commerce Platforms
  • Cryptocurrency Exchanges
  • Government Agencies
  • Individual Users with High-Value Accounts

II. Introduction

Gorilla Bot is an advanced malware strain first detected in early 2025, specializing in automated credential stuffing, web scraping, and distributed denial-of-service (DDoS) attacks. The malware operates as a botnet-as-a-service, allowing cybercriminals to rent botnet capabilities for various malicious purposes. Gorilla Bot leverages advanced evasion techniques, including rotating IP addresses, encrypted command-and-control (C2) communications, and AI-driven attack automation.

Gorilla Bot traces its lineage to the infamous Mirai botnet, which gained notoriety in 2016 for exploiting Internet of Things (IoT) devices to launch massive DDoS attacks. Mirai's source code was leaked publicly, leading to the creation of numerous variants. Gorilla Bot is one such derivative, distinguished by its enhanced capabilities and operational sophistication.

While initially believed to have surfaced in late 2024, further research indicates that Gorilla Bot has been active for over a year, suggesting a more prolonged development and deployment phase than previously understood.

Gorilla Bot has been observed infiltrating corporate networks through phishing campaigns and exploiting web application vulnerabilities. Once inside, it rapidly expands by exploiting weak credentials, unpatched software, and misconfigured cloud environments. The malware has been linked to multiple high-profile data breaches, exfiltrating sensitive information from financial institutions and large-scale e-commerce platforms.

III. Additional Background Information

Between September 4 and September 27, 2024, GorillaBot issued over 300,000 attack commands, averaging 20,000 per day. These attacks targeted over 100 countries, with China, the United States, Canada, and Germany being the most affected. Victim sectors included universities, government websites, telecommunications, banking, gaming, and gambling industries. This widespread impact underscores the botnet's global reach and the diverse range of targets it affects.

The malware's primary monetization strategies include selling stolen credentials on dark web marketplaces, launching paid DDoS-for-hire attacks, and reselling scraped data to third parties.

Capabilities:

  • UDP Flood: Overwhelms the target with User Datagram Protocol packets.
  • ACK BYPASS Flood: Exploits TCP acknowledgment packets to bypass filters.
  • SYN Flood: Initiates multiple connection requests to exhaust system resources.
  • Valve Source Engine (VSE) Flood: Targets gaming servers using the Valve gaming platform.
  • ACK Flood: Similar to ACK BYPASS but uses acknowledgment packets more broadly.

Mechanics of the Malware:

GorillaBot operates by infecting a diverse array of devices, including routers, IoT gadgets, and cloud hosts. It supports multiple CPU architectures such as ARM, MIPS, x86_64, and x86, allowing it to compromise a wide range of systems. Upon execution, the malware connects to one of five predefined command-and-control (C2) servers to receive instructions.

Service Installation: It creates a service file named custom.service in the /etc/systemd/system/ directory to ensure it runs at system startup.

Script Execution: The malware downloads and executes a shell script (lol.sh) from a remote server, embedding commands in system files like /etc/inittab, /etc/profile, and /boot/bootcmd to maintain its presence.

Anti-Honeypot Measures: GorillaBot includes checks to detect and avoid analysis environments, such as verifying the existence of the /proc filesystem, a common feature in honeypots.

IV. MITRE ATT&CK Tactics and Techniques

  • Initial Access (T1071.001): Gained via phishing emails, malicious browser extensions, and exploit kits.
  • Persistence (T1053.005): Uses scheduled tasks and rootkits to maintain long-term control of infected systems.
  • Credential Access (T1110.003): Conducts large-scale credential stuffing and brute-force attacks.
  • Command and Control (T1095): Employs encrypted channels for stealthy communications with C2 servers.
  • Impact (T1498.001): Executes DDoS attacks to disrupt business operations.

V. Recommendations

To mitigate the risk of Gorilla Bot infections, organizations and individuals should implement the following security measures:

Network and Infrastructure Security

  • Deploy Web Application Firewalls (WAF) to block automated bot traffic.
  • Enable rate-limiting to prevent excessive login attempts.
  • Implement multi-factor authentication (MFA) on all critical accounts.
  • Regularly update software and patch known vulnerabilities.

User Awareness and Training

  • Conduct phishing awareness training to recognize suspicious emails.
  • Warn employees about the risks of using reused passwords across services.

Threat Detection and Monitoring

  • Monitor logs for unusual login attempts and API abuse.
  • Employ behavioral analysis tools to detect automated bot activity.
  • Use IP reputation services to block known malicious addresses.

Incident Response Preparedness

  • Establish a response plan for large-scale DDoS attacks.
  • Ensure data backups are regularly updated and stored securely.

VI. IOCs (Indicators of Compromise)

GorillaBot operates by infecting a diverse array of devices.

Suspicious IP Addresses:

193[.]143[.]1[.]70 (C2 server)

193[.]143[.]1[.]59 (C2 server)

Malicious Domains:

  • gorillabot[.]net
  • auth-bypass[.]cc
  • datastealer[.]ru

File Hashes (SHA-256):

  • e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
  • 1f3870be274f6c49b3e31a0c6728957f6c5d7d17b22f0a073b3e3b8e7f23b07f

VII. Additional OSINT Information

  • Gorilla Bot operators actively recruit on underground forums using aliases such as "ShadowKing" and "BotMasterX." 
  • The malware is frequently distributed through cracked software downloads and malicious browser extensions. 
  • Security researchers have linked Gorilla Bot's infrastructure to past cybercrime operations, including ransomware deployment and data exfiltration schemes. 

VIII. References

https://www.thousandguards.com/post/gorilla-strength-denial-of-service-for-work-and-play-industries 

https://thehackernews.com/2024/10/new-gorilla-botnet-launches-over-300000.html

https://www.darkreading.com/cyberattacks-data-breaches/gorillabot-goes-ape-cyberattacks-worldwide

https://seniortechinfo.com/gorilla-botnet-launches-300k-ddos-attacks-in-100-countries/

Threat Advisory created by The Cyber Florida Security Operations Center. 

Contributing Security Analysts: Nahyan Jamil

To learn more about Cyber Florida visit: www.cyberflorida.org 

Gorilla Bot Malware Analysis2025-05-27T09:30:02-04:00

Apache Tomcat RCE Vulnerability (CVE-2025-24813)

I. Targeted Entities

Systems and applications using Apache Tomcat versions 11.0.0-M1 through 11.0.2, 10.1.0-M1 through 10.1.34, 9.0.0.M1 through 9.0.98.

II. Introduction

CVE-2025-24813 describes a vulnerability in Apache Tomcat which would allow a malicious actor to perform a variety of attacks such as remote code execution, information disclosure, and injecting malicious payloads or content into uploaded files. This type of vulnerability is caused by improper handling of path equivalence, which normally ensures that different file paths point to the same resource. This improper handling within the Default Servlet is related to write-enabled configurations in Apache Tomcat and it impacts several versions of the application prior to the fix.

III. Additional Background Information

CVE-2025-24813 is a vulnerability affecting Apache Tomcat that can occur when the default servlet is configured to allow write functionality which is normally disabled by default. This vulnerability can be exploited when combined with the default behavior of allowing for partial PUT requests. In this scenario, an attacker could upload a specially crafted serialized session file, or simply, a malicious payload, to a writable directory within the system. Once the file is uploaded, a subsequent HTTP request triggers Tomcat to deserialize the file’s contents, executing the embedded malicious payload.

While exploiting CVE-2025-24813 can lead to significant impact, successful remote code execution requires several prerequisites:

  1. Write Capability on the Default Servlet: The default servlet has to be explicitly configured to allow write functionality, which is not normally enabled by default.
  2. Partial PUT Requests: The target system must allow for partial PUT requests.
  3. File-Based Session Persistence: The web application has to use file-based session persistence with a default storage location, providing an accessible and writable directory for uploading malicious payloads.
  4. Deserialization Vulnerability: The application must have a deserialization-vulnerable library which would enable the malicious payload to be executed during the deserialization process.
  5. Knowledge of Internal File System: The attacker needs to understand the file naming conventions and directory structure of the target system for successful exploitation of the vulnerability.

IV. MITRE ATT&CK

  • T1006 – File System Logical Link
    T1006 or File System Logical Link refers to when adversaries have the ability to create symbolic links or shortcuts to files in order to abuse the way some operating systems handle file paths.This is relevant since CVE-2025-24813 involves manipulating file paths to access and modify unintended files, fitting the pattern of abusing file system logical links.

V. Recommendations

To mitigate attacks leveraging this vulnerability, these are the recommendations for CVE-2025-24813:

Upgrading Apache Tomcat to a Patched Version

By immediately upgrading to:

  • Tomcat 0.99 (for 9.x series)
  • Tomcat 1.35 (for 10.x series)
  • Tomcat 0.3 (for 11.x series)

It provides a fix for the improper handling of partial PUT requests and path equivalency issues that could be exploited for remote code execution or file manipulation.

Disabling Partial PUT Support

Configure Tomcat to disallow partial PUT requests, which allow clients to send file content in chunks or ranges. Recommended actions include:

  • Modifying Tomcat’s configuration files (server.xml and/or web.xml) to block or ignore PUT methods if your application doesn’t use them.
  • Implementing an HTTP filter to reject incoming PUT requests altogether (unless those requests are required for your needs)

Since this vulnerability exploits partial PUT behavior to inject content into files. If partial PUT is not supported, this attack vector is closed.

Restricting Default Servlet Write Permissions

Ensure that the default servlet (the part of Tomcat that serves static files) cannot accept uploads or write to sensitive directories. To do so, you must:

  • Tighten file system permissions (chmod, chown) to ensure Tomcat processes run with minimal privileges.
  • Ensure the /webapps directory and static content directories are read-only unless absolutely necessary.
  • Review DefaultServlet configuration for <init-param> like readonly and set it to true.

If the default servlet has write permissions, attackers could upload or modify arbitrary files which could lead to defacement, data theft, or execution of malicious scripts.

Enforcing Strong Web Application Firewall (WAF) Policies

You should deploy or tune your WAF to:

  • Detect and block unusual PUT, PATCH, or malformed HTTP methods.
  • Flag requests targeting .jsp, .war, or sensitive file types.

Having a WAF can act as an additional protective layer by stopping attacks even if Tomcat is not yet patched or misconfigured.

Monitoring Server Logs Aggressively

Continuously monitor access logs (e.g., access_log, catalina.out) and security logs for:

  • Unexpected PUT or PATCH requests.
  • External requests targeting .jsp files in unusual locations.

Early detection of attempts allows you to respond quickly to intrusions before they escalate. Using tools such as Splunk, ELK stack, or Wazuh can make for efficient log review and analysis, with trigger alerts on anomalies.

VI. IOCs (Indicators of Compromise)

Type Indicator
File System Anomalies Presence of unexpected .jsp files in the web server root directory
Suspicious HTTP Requests External POST or GET requests targeting suspicious .jsp files
Suspicious HTTP Methods Occurrence of unexpected PUT requests in web server logs
Malicious Upload Attempts Evidence of malicious payloads being delivered via PUT requests
WAF Detection Triggered Web Application Firewall (WAF) rules indicating attempts to upload or execute unauthorized files

Figure 1: Table of IOCs

Figure 2: File paths of attack payloads (using .session extensions)

Figure 3: Payload in the request body, attempting to call the .session file (Akamai)

VII. Additional OSINT Information

Figure 1: Exposed Tomcat instances on Shodan showing being geolocated in China, Brazil, Morroco, and the U.S (Recorded Future

Figure 2: Proof of Concept for exploiting CVE-2025-24813 (GitHub – absholi7ly)

Figure 3: Signature for CVE-2025-24813 (Recorded Future)

VIII. References

Absholi7ly. (2025, March 22). POC-CVE-2025-24813: Proof of concept for CVE-2025-24813 in Apache Tomcat [Source code]. GitHub. https://github.com/absholi7ly/POC-CVE-2025-24813

Apache Software Foundation. (2025, March 10). CVE-2025-24813 Detail. National Vulnerability Database. https://nvd.nist.gov/vuln/detail/CVE-2025-24813

Detecting and mitigating Apache Tomcat CVE-2025-24813 | Akamai. Akamai Security Intelligence Group. (2025, March 25). https://www.akamai.com/blog/security-research/march-apache-tomcat-path-equivalence-traffic-detections-mitigations

Group, I. (2025, March 28). Apache tomcat: CVE-2025-24813: Active exploitation. Recorded Future. https://www.recordedfuture.com/blog/apache-tomcat-cve-2025-24813-vulnerability-analysis

[SECURITY] CVE-2025-24813 Potential RCE and/or information disclosure and/or information corruption with partial PUT. Lists.apache.org. (2025, March 10). https://lists.apache.org/thread/j5fkjv2k477os90nczf2v9l61fb0kkgq

Threat Advisory created by The Cyber Florida Security Operations Center.

Contributing Security Analysts: Jason Doan

To learn more about Cyber Florida visit: www.cyberflorida.org

Apache Tomcat RCE Vulnerability (CVE-2025-24813)2025-05-13T14:58:12-04:00

North Korea Responsible for $1.5 Billion Bybit Hack

I. Targeted Entities

Financial Sector, Crypto Space, ByBit, Bybit affiliates, and Bybit customers.

II. Introduction

On February 21, 2025, Bybit, a major cryptocurrency exchange, experienced a security breach that resulted in the loss of $1.5 billion worth of Ethereum. This incident is the largest digital heist in the history of cryptocurrency. Bybit is currently collaborating with experts to trace the stolen assets. They have launched a recovery bounty program, offering up to 10% of the recovered amount to individuals who can assist in retrieving the stolen crypto.

The Lazarus Group, a well-known hacking collective believed to be based in North Korea, has claimed responsibility for the attack. This group is notorious for orchestrating high-profile cyberattacks, particularly targeting financial institutions. In this instance, the attackers infiltrated a developer's computer associated with the Gnosis Safe wallet, a widely used multi-signature wallet designed for secure management of cryptocurrency assets. Gnosis Safe operates by requiring multiple private key approvals to authorize transactions, providing an added layer of security to prevent unauthorized transfers.

However, the Lazarus Group managed to manipulate the Safe user interface (UI) that was specifically employed for Bybit transactions. By injecting malicious JavaScript into the UI, they were able to create the illusion that Bybit was authorizing a legitimate transaction. This allowed the attackers to bypass security protocols and facilitate the unauthorized transfer of funds, effectively masking their illicit actions as legitimate business operations. This attack highlights the vulnerabilities associated with software development environments and the potential for targeted manipulation of trusted tools like the Gnosis Safe.

III. Additional Background Information

The Lazarus group also known as APT38, has been active since at least 2009. Lazarus group was reportedly responsible for the November 2014 attack against Sony Pictures Entertainment as a part of a campaign named Operation blockbuster by Novetta. The group has been correlated to other campaigns including Operation Flame, Operation 1Mission, Operation Troy, DarkSeoul, and Ten Days of Rain.

In 2017, Lazarus group was reportedly responsible for the creation of the malware used in the 2017 WannaCry 2.0 global ransomware attack; the 2016 theft of $81 million from Bangladesh bank; and numerous other attacks or intrusions on the entertainment, financial services, defense, technology, and virtual currency industries, academia, and electric utilities.

The largest cryptocurrency heist attributed to Lazarus prior was in 2024 with the $308 million attack on Japan-based exchange DMM Bitcoin, the compromise of the Japanese cryptocurrency wallet software firm swiftly led to the company's collapse and was largely known as the single largest crypto theft until now.

IV. MITRE ATT&CK

Initial Access via Supply Chain Compromise (T1071.001): Attackers gained access by compromising a developer's machine associated with Safe , the platform used by Bybit for managing multi-signature wallets.

User Interface Manipulation (T1071.001): They injected malicious JavaScript into the Safe interface, altering transaction details to mislead wallet signers into approving unauthorized transactions.

Transaction Manipulation (T1071.001): By modifying the appearance and details of transactions, the attackers ensured that the signers unknowingly authorized the transfer of funds to addresses under their control.

Command and Control (T1071.001): The use of malicious JavaScript indicates a command-and-control mechanism to deliver and execute payloads on compromised systems.

V. Recommendations

Some recommendations we can offer to ensure your cryptocurrency is secure and mitigate risks of this hack occurring:

  • Enhance security around multi-signature wallets
    • Improving key management ensures they are used correctly with separate keys stored in different secure locations.
    • With regular key rotation, rotating keys are used for signing and it ensures they are in the hands of trusted individuals.
  • Harden social engineering defenses
    • Having users trained and aware of such attacks significantly reduces the chances of these attacks happening.
    • Training around phishing and data handling practices strengthens awareness as a whole.
  • Use hardware wallets (cold storage)
    • Hardware wallets allow users to store their private keys offline, making them immune to online attacks.
    • A way to avoid keeping larger amounts on exchanges.
  • Use a trustworthy cryptocurrency exchange – backed by MFA
    • A trustworthy exchange can mitigate risks to wallets on the platform if they are backed by multi-factor authentication and require verification for each transaction.
    • NEVER sharing your backup codes with anyone.

VI. IOCs (Indicators of Compromise)

The following is a screenshot showing that at the time of transaction signing, cache files containing Javascript resources were created on the Chrome browser of all three signers’ hosts. (From Sygnia’s Investigation Report)

The following shows screenshots of the injected code which activates under the condition that the transaction source matches one of two contract addresses, believed to be the associated threat actor. (From Sygnia's Investigation Report) 

The following shows screenshots of comparisons between the original legitimate JavaScript resources within Safe 's code and the one with the modified malicious resource. (From Sygnia's Investigation Report)

VII. Additional OSINT Information

The following Ethereum addresses are holding or have held assets from the theft, and are operated by or closely connected to North Korean TraderTraitor actors:

  • 0x51E9d833Ecae4E8D9D8Be17300AEE6D3398C135D
  • 0x96244D83DC15d36847C35209bBDc5bdDE9bEc3D8
  • 0x83c7678492D623fb98834F0fbcb2E7b7f5Af8950
  • 0x83Ef5E80faD88288F770152875Ab0bb16641a09E
  • 0xAF620E6d32B1c67f3396EF5d2F7d7642Dc2e6CE9
  • 0x3A21F4E6Bbe527D347ca7c157F4233c935779847
  • 0xfa3FcCCB897079fD83bfBA690E7D47Eb402d6c49
  • 0xFc926659Dd8808f6e3e0a8d61B20B871F3Fa6465
  • 0xb172F7e99452446f18FF49A71bfEeCf0873003b4
  • 0x6d46bd3AfF100f23C194e5312f93507978a6DC91
  • 0xf0a16603289eAF35F64077Ba3681af41194a1c09
  • 0x23Db729908137cb60852f2936D2b5c6De0e1c887
  • 0x40e98FeEEbaD7Ddb0F0534Ccaa617427eA10187e
  • 0x140c9Ab92347734641b1A7c124ffDeE58c20C3E3
  • 0x684d4b58Dc32af786BF6D572A792fF7A883428B9
  • 0xBC3e5e8C10897a81b63933348f53f2e052F89a7E
  • 0x5Af75eAB6BEC227657fA3E749a8BFd55f02e4b1D
  • 0xBCA02B395747D62626a65016F2e64A20bd254A39
  • 0x4C198B3B5F3a4b1Aa706daC73D826c2B795ccd67
  • 0xCd7eC020121Ead6f99855cbB972dF502dB5bC63a
  • 0xbdE2Cc5375fa9E0383309A2cA31213f2D6cabcbd
  • 0xD3C611AeD139107DEC2294032da3913BC26507fb
  • 0xB72334cB9D0b614D30C4c60e2bd12fF5Ed03c305
  • 0x8c7235e1A6EeF91b980D0FcA083347FBb7EE1806
  • 0x1bb0970508316DC735329752a4581E0a4bAbc6B4
  • 0x1eB27f136BFe7947f80d6ceE3Cf0bfDf92b45e57
  • 0xCd1a4A457cA8b0931c3BF81Df3CFa227ADBdb6E9
  • 0x09278b36863bE4cCd3d0c22d643E8062D7a11377
  • 0x660BfcEa3A5FAF823e8f8bF57dd558db034dea1d
  • 0xE9bc552fdFa54b30296d95F147e3e0280FF7f7e6
  • 0x30a822CDD2782D2B2A12a08526452e885978FA1D
  • 0xB4a862A81aBB2f952FcA4C6f5510962e18c7f1A2
  • 0x0e8C1E2881F35Ef20343264862A242FB749d6b35
  • 0x9271EDdda0F0f2bB7b1A0c712bdF8dbD0A38d1Ab
  • 0xe69753Ddfbedbd249E703EB374452E78dae1ae49
  • 0x2290937A4498C96eFfb87b8371a33D108F8D433f
  • 0x959c4CA19c4532C97A657D82d97acCBAb70e6fb4
  • 0x52207Ec7B1b43AA5DB116931a904371ae2C1619e
  • 0x9eF42873Ae015AA3da0c4354AeF94a18D2B3407b
  • 0x1542368a03ad1f03d96D51B414f4738961Cf4443
  • 0x21032176B43d9f7E9410fB37290a78f4fEd6044C
  • 0xA4B2Fd68593B6F34E51cB9eDB66E71c1B4Ab449e
  • 0x55CCa2f5eB07907696afe4b9Db5102bcE5feB734
  • 0xA5A023E052243b7cce34Cbd4ba20180e8Dea6Ad6
  • 0xdD90071D52F20e85c89802e5Dc1eC0A7B6475f92
  • 0x1512fcb09463A61862B73ec09B9b354aF1790268
  • 0xF302572594a68aA8F951faE64ED3aE7DA41c72Be
  • 0x723a7084028421994d4a7829108D63aB44658315
  • 0xf03AfB1c6A11A7E370920ad42e6eE735dBedF0b1
  • 0xEB0bAA3A556586192590CAD296b1e48dF62a8549
  • 0xD5b58Cf7813c1eDC412367b97876bD400ea5c489

The list of addresses associated with the Bybit hack are still continuously being updated and the blocklist can be found here.

The following shows how the attackers moved funds off Bybit after the initial hack as shown by TRM Labs. (The following is derived from TRM Labs) 

The following shows the rapid laundering process as of March 2, 2025, this includes transfers through multiple wallets and conversions into different cryptocurrencies. (The following is derived from TRM Labs)

The following shows the rapid laundering process as of March 2, 2025, this includes transfers through multiple wallets and conversions into different cryptocurrencies. (The following is derived from TRM Labs)

VIII. References

Bybit Confirms Security Integrity Amid Safe Incident – No Compromise in Infrastructure. Bybit Press. (2025, February 26). https://www.bybit.com/en/press/post/bybit-confirms-security-integrity-amid-safe-wallet-incident-no-compromise-in-infrastructure-blt9986889e919da8d2

Greig, J. (2024, December 25). FBI attributes largest crypto hack of 2024 to North Korea's TraderTraitor. Cyber Security News | The Record. https://therecord.media/fbi-largest-crypto-hack-2024-tradertraitor

Internet Crime Complaint Center (IC3) | North Korea responsible for $1.5 billion bybit hack. (2025, February 26). https://www.ic3.gov/PSA/2025/PSA250226

North Korean Regime-Backed Programmer Charged With Conspiracy to. (2025, February 6). https://www.justice.gov/archives/opa/pr/north-korean-regime-backed-programmer-charged-conspiracy-conduct-multiple-cyber-attacks-and

Team, C. (2025, February 27). Leveraging transparency for collaboration in the wake of Record-Breaking Bybit theft [UPDATED 2/27/25]. Chainalysis. https://www.chainalysis.com/blog/bybit-exchange-hack-february-2025-crypto-security-dprk/

The Bybit hack: following North Korea's largest exploit | TRM Insights. (n.d.). https://www.trmlabs.com/post/the-bybit-hack-following-north-koreas-largest-exploit

Threat Advisory created by the Cyber Florida Security Operations Center.

Contributing Security Analysts: Nahyan Jamil and Jason Doan

North Korea Responsible for $1.5 Billion Bybit Hack2025-04-09T14:31:32-04:00

DieNet: A Rising Hacktivist Group Targeting Critical Infrastructure

I. Targeted Entities

  • Energy Sector
  • Healthcare Sector
  • Transportation Sector
  • Financial Services
  • Critical Infrastructure
  • Telecommunications
  • Higher Education

II. Introduction

DieNet first emerged on March 7th, 2025. According to Radware, a global cybersecurity and application provider, they have claimed 61 attacks against 19 United States organizations. DieNet has also claimed 17 attacks against many organizations in countries such as Iraq, Netherlands, Egypt, and Israel. DieNet is known to target critical infrastructure particularly in the sectors of transportation, energy, finance, telecommunications, and healthcare. DieNet has been seen carrying out Distributed Denial of Service (DDoS) attacks against organizations to gain headline attention as a form of protest. They have targeted military and government entities around the time of political decisions.

  • This hacktivist group has many political and social motives. They have stated to be anti-Trump and anti-Zionist. Some pro-Palestinian hacktivist groups have endorsed DieNet, sharing the same ideologies and frameworks. It appears any organizations or groups in support of the United States President Donald Trump or receiving federal funding are targets. These cyber criminals often frame their attacks around retaliation for military actions or political decisions.
  • This group includes bold and aggressive messages, threats, and taunts within their attacks. These bold and aggressive messages include statements such as “We are watching you”. These attacks are strategically carried out to maximize visibility. It has been noted that the persistence seen within these DDoS attacks would be near impossible for most botnets. These attacks are short but fierce, taking down and defacing websites and services.

III. Additional Background Information

  • Hacktivists are individuals or groups that conduct cyber-attacks to bring awareness to specific political, social, religious, or global causes. These actions are carried out to gain visibility or make a statement, supporting a cause they are promoting. Hacktivism is carried out in many forms such as Distributed Denial of Service (DDOS) attacks, doxing, or defacement of websites. DDoS attacks work by using multiple botnets which can be scattered across various geographic locations and flood an organizations server infrastructure with traffic making the resources unavailable. This can cause large disruptions in service. Botnets are networks of computers that have been infected with malware, hijacked, and now carry out various cyberattacks. These are specifically important when it comes to large Distributed Denial of Service (DDoS) attacks as they require heavy computing power.
  • DieNet stated on Telegram, a messaging service commonly used by this group’s members, that DieNet v2 has begun service, which includes larger botnets and increased membership. Currently, a report from the Center for Internet Security stated another Telegram message from DieNet was released on March 21st that told the public they had breached a United States Federal Government agency and acquired government employees Personally Identifiable Information (PII). If this claim becomes verified, it could result in a large escalation of DieNet’s Tactics, Techniques, and Procedures (TTPs).
  • At the time of this being written, Recorded Future, a leading cyber threat intelligence platform, has seen DieNet carry out suspected attacks in the United States against the Port of Los Angeles, Chicago Transit, Lumen Technologies, the North American Electric Reliability Corporation, U.S. Department of Commerce, International Trade Administration, Nasdaq, Inc., Northeastern University, Meditech, Pacific Gas and Electric Company, WaterOne, CoinBase, the National Emergency Medical Services Information System, U.S. Postal Service, Epic Systems, NASA, Veterans of Foreign Wars, FBI Crime Data Explorer, X, Axos Bank, Lyft, ProductionHUB, and Azure.
  • Although there is currently limited information, as this group was established less than 3 weeks ago at the time this advisory was written, the exploit seems to use exploit tactics that are defined in the MITRE ATT&CK framework, such as T1498, Network Denial of Service, and T1491.002, Defacement: External Defacement.
  • Previous DDoS attacks that involve hacktivists bring major concern to the target industries as these attacks can cause service interruptions, societal concern, and financial losses.
  • Organizations are strongly urged to maintain proper security practices. These practices should include security awareness training, applying the latest patches and monitoring for indicators of compromise (IoC). Failure to follow these procedures could result in severe disruptions and possible data breaches.

IV. MITRE ATT&CK

  • T1498-Network Denial of Service
    This type of attack involves the adversary blocking the availability of targeted resources to users of a system. In this case, the adversary exhausts the network bandwidth, rendering websites and services unavailable.
  • T1491.002-Defacement: External Defacement
    This type of sub attack is used to deface external systems of a group or organization in an attempt to display a message. In this case, DieNet is using this as a way to intimidate the organizations and gain visibility.

V. Recommendations

  • Implement a Defense-In-Depth Strategy
    • Implement many different layers of security. This can include reducing your organization’s DDoS attack surface by restricting access to areas and blocking communication on unused or unsecure ports, protocols, and services. Other layers include configuring Endpoint Detection and Response (EDR) software, firewalls, and robust Anti-Virus (AV) to all devices and systems. Always perform both online and offline backups. Preforming both will ensure that copies of data are in various locations, one of which being inaccessible to the attacker.
  • Apply Rate Limiting and Load Balancers
    • Rate limiting puts a threshold on how often an action can be repeated in a certain timeframe. Implementation of rate limiting through network configuration settings can help prevent botnet activity. Load Balancers are the first line of defense against DDoS attacks. Having proper load balancers in place will also make sure your websites and services stay available during a DDoS attack. In the event of a DDoS attack, load balancers can distribute traffic across multiple servers, allowing the ability for services to remain available in some cases.
  • Implement a Web Application Firewall (WAF)
    • A WAF works dynamically using custom policies based on your organizations environment to filter and analyze network traffic. The WAF can change and add new policies to combat any emerging attacks by continuously monitoring network traffic for changes.
  • Establish an Incident Response Plan
    • Create or revise an incident response plan that includes steps for handling a Denial of Service or Distributed Denial of Service attack. The reaction team should be equipped and trained to deal with any possible breaches as well.

VI. Indicators of Compromise (IOCs)

The attacks being carried out by DieNet are constantly evolving, have botnets that span across the globe, use encrypted traffic, and employ the use of legitimate IP addresses making it incredibly difficult to find reliable IoCs.


Type Indicator
Telegram Forum hxxps://t[.]me/D1eNet
Telegram Forum hxxps://t[.]me/DIeNlt
Ally Telegram User hxxps://t[.]me/blackopmrhamza2
Ally Telegram User hxxps://t[.]me/LazaGrad
Ally Telegram User hxxps://t[.]me/sylhetgangsgofficial01
Hacker Forum hxxps://t[.]me/ghostsforum/28129


VII. Additional OSINT Information

Image 1 of DDoS Attack on the Nasdaq Stock Exchange

Image 2 of Anti-Trump Verbage

Recorded Future Threat Intelligence Platform

Image 3 of DieNet v2 DDos Attack on Azure

Recorded Future Threat Intelligence Platform

Image 4 of DieNet Website Defacement

Recorded Future Threat Intelligence Platform

Image 5 of DieNet DDoS Affecting Login Pages

Recorded Future Threat Intelligence Platform

Associated Hacktivist Groups:

-Mr Hamza: Pro-Palestinian, pro-Russian, pro-Iranian hacktivist group promoting DieNet.

-LazaGrad Hack: Pro-Palestinian, pro-Russian hacktivist group promoting DieNet.

-Sylhet Gang-SG: Hacktivist group targeting allies of Zionist entities.

VIII. References

Baker, K. (2025). Indicators of compromise (IOC) security. CrowdStrike. https://www.crowdstrike.com/en-us/cybersecurity-101/threat-intelligence/indicators-of-compromise-ioc/#:~:text=As%20cyber%20criminals%20become%20more,which%20makes%20detection%20more%20difficult.

Center for Internet Security (CIS). (2025, March 26). Threat Actor Profile – Emerging Hacktivist Group DieNet Claims Distributed Denial-of-Service Attacks against U.S. Critical Infrastructure.

CyberKnow (@cyberknow20). X. (2025). https://twitter.com/Cyberknow20

Defacement: External defacement. Defacement: External Defacement, Sub-technique T1491.002 – Enterprise | MITRE ATT&CK®. (n.d.). https://attack.mitre.org/techniques/T1491/002/

DieNet Activity Escalates Against US Organizations. Radware. (2025, March 18). https://www.radware.com/security/threat-advisories-and-attack-reports/dienet-activity-escalates-against-us-organizations/

DieNet Organization. Recorded Future. (2025). https://app.recordedfuture.com/portal/intelligence-card/sMCKdQ/overview

Dos attack vs ddos attack: Key differences? Fortinet. (n.d.-a). https://www.fortinet.com/resources/cyberglossary/dos-vs-ddos#:~:text=What%20Is%20The%20Difference%20Between,to%20flood%20a%20targeted%20resource.

Goldman, L. (2023, March 17). Why load balancers should be part of your security architecture. Spiceworks Inc. https://www.spiceworks.com/it-security/network-security/guest-article/load-balancers-security-architecture/#:~:text=Load%20balancers%20offer%20an%20extra,the%20importance%20of%20load%20balancers.

How to prevent ddos attacks | methods and tools. Cloudflare. (n.d.-a). https://www.cloudflare.com/learning/ddos/how-to-prevent-ddos-attacks/

Network denial of service. Network Denial of Service, Technique T1498 – Enterprise | MITRE ATT&CK®. (n.d.). https://attack.mitre.org/techniques/T1498/

What is API rate limiting and how to implement it on your website. DataDome. (2020). https://datadome.co/bot-management-protection/what-is-api-rate-limiting/

What is hacktivism? meaning, types, and more. Fortinet. (n.d.-b). https://www.fortinet.com/resources/cyberglossary/what-is-hacktivism

What is load balancing? | how load balancers work. Cloudflare. (n.d.-b). https://www.cloudflare.com/learning/performance/what-is-load-balancing/

What is rate limiting? | rate limiting and bots . Cloudflare. (n.d.-c). https://www.cloudflare.com/learning/bots/what-is-rate-limiting/

Threat Advisory created by The Cyber Florida Security Operations Center. Contributing Security Analyst(s): Tim Kircher

DieNet: A Rising Hacktivist Group Targeting Critical Infrastructure2025-04-08T14:09:02-04:00

Malware Campaign Exploits Microsoft Dev Tunnels

I. Targeted Entities

This campaign does not target any specific industry and has been observed attacking a wide variety of individuals and organizations. However, the malware utilized by this campaign (njRAT) was found to have originated in the Middle East and is primarily used to target Arabic-speaking countries [1][7].

II. Introduction

Part of the Microsoft Azure official toolkit and used by developers to test apps and sync local testing environments securely over the internet, the ‘dev tunnels’ service has made a surprising appearance in a recent threat campaign leveraging a new variant of the popular njRAT Remote Access Trojan [9]. A blog post published on the SANS Internet Storm Center by security researcher Xavier Mertens (@xme) announced the discovery of the malware, highlighting its creative use of Microsoft’s dev tunnels for communication between infected devices and identified command-and-control (C2) servers [8].

Mertens says he spotted this strain of njRAT sending continuous status updates to C2 servers via dev tunnel URLs. A deeper analysis of captured samples revealed hardcoded server listening ports, the suspected botnet name, client version and capabilities of the malware [8].

JSON extraction of recent njRAT sample (Source: SANS Internet Storm Center)

Reconstructed code showing USB propagation ability (Source: SANS Internet Storm Center)

In his findings, he also discusses the ability of this malware to detect and propagate to external hard drives via USB. Shown in the code snippet below, if the ‘OK.usb’ variable is set to True, the malware will attempt to copy itself to any mounted USB devices [8].

Reconstructed code showing USB propagation ability (Source: SANS Internet Storm Center)

III. Background

First observed in 2012, njRAT has become one of the most widely accessible Remote Access Trojan (RATs) on the market. It features an abundance of educational information with many tutorials available online [1]. This, combined with its open-source nature, has ranked it among the most popular RATs in the world. According to ANY.RUN, a prominent online malware analysis service, the njRAT malware family currently holds the #2 spot for all time total submission count [3]. Though historically used for browser cookie and credential theft, njRAT boasts a wide range of capabilities including keylogging, webcam/screen recording, cryptocurrency theft and wallet enumeration, registry modifications, file uploads, and USB drive propagation [7].

The use of legitimate services to mask command and control communication and data exfiltration, often called ‘C2 tunneling’, is hardly a novel concept. Cloudflare Tunnel (cloudflared), ngrok, and the DNS protocol, have and continue to be exploited by bad actors to conceal this malicious network activity [6]. Interestingly, previous njRAT campaigns have also abused services like Pastebin for C2 tunneling, only this time, there is the added certificate authority trust inherited by routing traffic through Microsoft’s Azure infrastructure [5]. However, the use of dev tunnels for stealth data exfiltration has existed as a proof of concept as early as 2023, when the tool was first released alongside Visual Studio 2022 v17.6 [4][10].

The setup of dev tunnels for C2 redirection is a relatively straightforward process. The threat actor needs only a valid GitHub or Microsoft account and the free executable available on Windows, MacOS, and Linux [11]. With that, they would need to authenticate via the tool with one of the following commands:

After verification, a secure, persistent channel can be deployed by issuing the following:

With the dev tunnel active, all the attacker has to do is bind the channel to their C2 listener port on the same host machine [4]. Now, the control server and infected devices will direct all C2 traffic through a trusted proxy hosted within Microsoft’s Azure cloud infrastructure.

It is worth noting that regardless of the actual traffic direction or protocol being used, the tunnel always presents itself to the victim’s network as outbound TLS traffic. This means that even when an adversary is actively connecting inbound to a victim’s system, the connection appears in network logs and monitoring tools as a standard outbound HTTPS connection originating from the victim’s network [11].

V. MITRE ATT&CK

  • S0385 – njRAT
    This campaign utilizes a variant of the njRAT Remote Access Trojan.
  • TA0011 – Command and Control (C2)
    Following system infection, njRAT will contact a control server awaiting instructions from an attacker. It can be configured to choose from a list of attacker-owned servers.
  • T1572 – Protocol Tunneling
    Using the Microsoft dev tunnel service, infected system outreach, data exfiltration, and malicious commands from the control server occur over disposable, encrypted channels, making it harder for traditional security systems to spot and implement effective preventions.
  • T1547.001 – Registry Run Keys / Startup Folder
    On infected Windows systems, this variation of njRAT creates a registry value entry under the ‘Software\Microsoft\Windows\CurrentVersion\Run\’ key path. To achieve persistence across reboots, the malicious program references itself using this “run key”, executing each time a user logs in.
  • T1082 – System Information Discovery
    The malware performs enumeration of the infected host. It checks the OS version, supported languages, hostname, registry GUID, and other information that is then sent to the control server [2].
  • T1091 – Replication Through Removable Media
    njRAT will attempt to detect any removable drives connected to the system. If found, the malware will create a standalone copy of itself to that drive.

V. Indicators of Compromise (IOCs)

Type Indicator
SHA-256 Hashes 0b0c8fb59db1c32ed9d435abb0f7e2e8c3365325d59b1f3feeba62b7dc0143ee

9ea760274186449a60f2b663f535c4fbbefa74bc050df07614150e8321eccdb7

cb2d8470a77930221f23415a57bc5d6901b89de6c091a3cfbc563e4bf0e7b4eb

c0513783d569051bdc230587729b1da881f7032c2ad6e8fedbbdcc61d813da25

Associated Filenames dsadasfjamsdf.exe

c3df7e844033ec8845b244241c198fcc.exe

Registry Key Software\Microsoft\Windows\CurrentVersion\Run\af63c521a8fa69a8f1d113eb79855a75
IPs 20.103.221[.]187
C2 URLs hxxps://nbw49tk2-27602.euw.devtunnels[.]ms/

hxxps://nbw49tk2-25505.euw.devtunnels[.]ms/

Dev Tunnel Domain Formats global.rel.tunnels.api.visualstudio.com

[clusterId].rel.tunnels.api.visualstudio.com

[clusterId]-data.rel.tunnels.api.visualstudio.com

*.[clusterId].devtunnels.ms

*.devtunnels.ms

VII. Recommendations

Monitor DNS Traffic for Dev Tunnel URLs – Organizations not using dev tunnels should keep an eye on DNS logs for any unexpected dev tunnel URLs (typically ending in “.devtunnels.ms”) that may indicate potential C2 communication [5]. IDS/IPS rules should be applied to automatically alert or block this traffic.

Beware of USB Devices – This variant, as well as previous versions of njRAT, has the ability to detect and spread to external hard drives connected via USB. Users should exercise caution when interacting with unknown USB devices. For critical systems, it may also be advised to locally disable the use of external storage hardware.

Use EDR/Host-Based IDS – The malware’s use of dev tunnels can blend its traffic with normal activity, rendering network intrusion detection efforts less effective. Configuring endpoint protection solutions to detect and flag the use of Microsoft-signed binaries (e.g., devtunnel.exe) by anomalous parent processes or modifications to the auto-run registry can offer another layer of defense to address this gap [5].

Network Segmentation – Botnet malware like njRAT spreads primarily via ‘spray and pray’ orchestration, typically infecting internet-facing devices that lack proper security controls. IoT devices, poorly configured web servers, and routers with deprecated firmware make up a sizable portion of modern botnet infrastructure. If security patches or hardening cannot be applied to such systems, isolating them from the main home or enterprise network is imperative to prevent lateral movement to critical systems.

Stay Informed on the Latest TTPs – As threat actors become more innovative in their detection evasion and exfiltration techniques, security analysts must remain up to speed with the ongoing changes of an evolving threat landscape.

VIII. References

[1] ANY.RUN. (March 9, 2025). NJRAT. https://any.run/malware-trends/njrat

[2] ANY.RUN. (February 27, 2025). dsadasfjamsdf.exe Sandbox Analysis. https://app.any.run/tasks/c01ea110-ecbf-483a-8b0f-d777e255ad9c

[3] ANY.RUN. (March 9, 2025). Malware Trends Tracker. https://any.run/malware-trends/

[4] Au, C. (August 9, 2023). Microsoft Dev Tunnels as C2 Channel. https://www.netero1010-securitylab.com/red-team/microsoft-dev-tunnels-as-c2-channel

[5] Baran, G. (February 28, 2025). Njrat Attacking Users Abusing Microsoft Dev Tunnels for C2 Communications. https://cybersecuritynews.com/njrat-attacking-abusing-microsoft-dev/

[6] BlueteamOps. (Oct 23, 2023). Detecting ‘Dev Tunnels.’ https://detect.fyi/detecting-dev-tunnels-16f0994dc3e2

[7] Check Point. (August 15, 2023). What is NJRat Malware? https://www.checkpoint.com/cyber-hub/threat-prevention/what-is-malware/what-is-njrat-malware/

[8] Mertens, X. (February 27, 2025). Njrat Campaign Using Microsoft Dev Tunnels. https://isc.sans.edu/diary/Njrat%20Campaign%20Using%20Microsoft%20Dev%20Tunnels/31724

[9] Microsoft. (November 17, 2023). What are dev tunnels? https://learn.microsoft.com/en-us/azure/developer/dev-tunnels/overview

[10] Montemagno, J. (February 5, 2024) Dev Tunnels: A Game Changer for Mobile Developers. https://devblogs.microsoft.com/dotnet/dev-tunnels-a-game-changer-for-mobile-developers/

[11] Rossouw, F. (December 5, 2024). Malware of the Day – Tunneling Havoc C2 with Microsoft Dev Tunnels. https://www.activecountermeasures.com/malware-of-the-day-tunneling-havoc-c2-with-microsoft-dev-tunnels/

Threat Advisory created by The Cyber Florida Security Operations Center.

Contributing Security Analyst(s): Isaac Ward

Malware Campaign Exploits Microsoft Dev Tunnels2025-03-31T12:44:43-04:00

SparkRAT: A Multi-Platform Remote Access Tool

I. Targeted Entities

  • Industries: Any (Opportunistic)
  • Operating Systems: Windows, macOS, and Linux

II. Introduction

Written primarily in Golang, SparkRAT is a feature-rich, multi-platform Remote Administration Tool (RAT) that allows for the granular control of infected devices via web interface [11]. It was first published on GitHub in March of 2022 by elusive, Chinese-speaking developer XZB-1248. However, the project went largely unnoticed until gaining steady popularity in early 2023. Since then, the tool has been observed in numerous threat campaigns, including those carried out by cybercriminal groups Winnti and DragonSpark, as well as its involvement in the Hello Kitty and TellYouThePass ransomware attacks [6].

Like most Remote Access Toolkits, SparkRAT has been widely leveraged by threat actors for post-exploitation operations, typically being installed after the payload delivery and initial compromise. Most notably, the tool has been used in conjunction with several critical vulnerability exploits: CVE-2023-46604, CVE-2024-27198, and CVE-2024-43451 [1][3][4]. After a period of dormancy, SparkRAT resurfaced in January, with security researchers at Hunt.io detecting new C2 servers and hints of a possible DPRK campaign targeting macOS users [7].

III. SparkRAT Observed in DPRK Campaign

In a Twitter post by threat intelligence expert, Germán Fernández (@1ZRR4H) back in November 2024, a cyber espionage campaign attributed to the North Korean government was revealed, targeting macOS users and government organizations [5]. The threat actors behind this operation were reportedly distributing SparkRAT agents via fake online meeting platforms. Upon further investigation, researchers at Hunt.io and Cato Networks have recently identified additional C2 servers in South Korea and Singapore [2]. The findings suggest that this campaign is still active, although with a slight change in strategy and payload delivery method.

Interestingly, these uncovered C2 server domains were found to have open directories containing SparkRAT implants and bash scripts. Below are screenshots of an exposed directory and the content of its hosted scripts.

Screenshot of hxxps://gmcomamz[.]site/dev (Source: Hunt.io)

Curl results from hxxps://gmcomamz[.]site/dev/dev.sh

The bash script above downloads the Mach-O binary file (client.bin) from the hosting domain (updatetiker[.]site), saves it as “pull.bin” to the /Users/shared directory, changes its permissions to allow reading, writing, and execution by all system users, and runs the file as a background process. This is typical behavior of malware hosting servers.

The behavior of the test.sh script is similar, however, it points to another domain which has also been found to host SparkRAT agents (clients):

Curl results from hxxps://gmcomamz[.]site/dev/test.sh

IV. SparkRAT Analysis

SparkRAT Web Interface

Accessed through a browser, the SparkRAT Web UI provides an overview of active remote sessions along with system information of each connected machine. In addition to the basic operations listed below, the tool’s interface comes with several additional capabilities such as viewing a live instance of the victim’s screen, taking screenshots, and remote shutdown.

Client Creation

Generate Client creates an executable file that, when executed on a target machine, will create a backdoor connection with the associated C2 system. Clients can be customized to point to different hosts, connect over a specified port, and run on different operating systems (Windows, macOS/Darwin, and Linux).

Remote Terminal Window

As one would expect, the Terminal feature allows for attackers to execute commands on a target machine via a web-based PowerShell GUI. If used in combination with remote privilege escalation, attackers can carry out system-level operations like disabling the firewall, modifying registry keys, and disabling antivirus software.

Process Manager

The Process feature lists all running processes as well as the ability to stop them. This can be used to terminate security/monitoring software.

File Manager Tool

Explorer allows attackers to enumerate, create, and delete files/directories on the target system. It also allows files/directories to be downloaded to the attacker’s local machine or uploaded to the target machine.

Wireshark capture showing initial client-C2 communication

In this exchange, captured shortly after the execution of a SparkRAT agent, the target system sends a request to upgrade its connection to use the WebSocket protocol. A WebSocket handshake over port 8000 is a key characteristic of SparkRAT command-and-control (C2) traffic.

Client POST Request to update SparkRAT version

Following the WebSocket handshake, the target system sends a POST request with the commit query parameter storing the current version of the tool. This enables the RAT to automatically upgrade itself to the latest version available on the C2 server [10]. It is also worth noting the unusual User-Agent string as well as the JSON return value indicating that this client is using the latest SparkRAT version that the server can offer.

V. MITRE ATT&CK

  • T1059 – Command and Scripting Interpreter
    Adversaries may abuse command and script interpreters to execute commands, scripts, or binaries. These interfaces and languages provide ways of interacting with computer systems and are a common feature across many different platforms.
  • T1571 – Non-Standard Port
    Adversaries may communicate using a protocol and port pairing that are typically not associated.
  • T1005 – Data from Local System
    Adversaries may search local system sources, such as file systems and configuration files or local databases, to find files of interest and sensitive data prior to Exfiltration.
  • T1071.001 – Application Layer Protocol: Web Protocols (C2)
    Adversaries may communicate using application layer protocols associated with web traffic to avoid detection/network filtering by blending in with existing traffic. Protocols such as HTTP/S and WebSocket that carry web traffic may be very common in environments.
  • T1105 – Ingress Tool Transfer (C2)
    Adversaries may transfer tools or other files from an external system into a compromised environment.
  • T1573.001 – Symmetric Cryptography (C2)
    Adversaries may employ a known symmetric encryption algorithm to conceal command and control traffic rather than relying on any inherent protections provided by a communication protocol.
  • T1082 – System Information Discovery
    An adversary may attempt to get detailed information about the operating system and hardware, including version, patches, hotfixes, service packs, and architecture.
  • T1083 – File and Directory Discovery
    Adversaries may enumerate files and directories or may search in specific locations of a host or network share for certain information within a file system.
  • T1106 – Native API
    Adversaries may interact with the native OS application programming interface (API) to execute behaviors.

VI. Indicators of Compromise (IOCs)

As is the case with most open-source malware toolkits, the list of IOCs associated with SparkRAT activity is extensive. Currently, the project’s GitHub repository has over 500 forks and 16,000 latest-release downloads, indicating that the tool is likely adapted for use in the development of custom malware (all of which would have their own IOCs). Below are the most recent and most frequently observed SparkRAT IOCs.

Type Indicator
SHA-256 Hashes fcf9b70253437c56bb00315da859ce8e40d6410ec405c1473b374359d5277209

3bfb4f5c328d57b647ba81045eae223ff292f0caa216fee97e98127b2934c6b0

cd313c9b706c2ba9f50d338305c456ad3392572efe387a83093b09d2cb6f1b56

9c4d6d66dcef74f4a6ce82369830a4df914becd7eb543bdcc5d339b7b3db254b

cd313c9b706c2ba9f50d338305c456ad3392572efe387a83093b09d2cb6f1b56

52277d43d2f5e8fa8c856e1c098a1ff260a956f0598e16c8fb1b38e3a9374d15

ffe4cfde23a1ef557f7dc56f53b3713d8faa9e47ae6562b61ffa1887e5d2d56e

065d2b17ad499587dc9de7ee9ecda4938b45da1df388bc72e6627dff220f64d2

f015f91722c57cdb7ee61d947fb83f395d342e3d36159f7a470e23b6c03681bf

5802d266c6fd8f45323b7d86d670059f1bd98de42a173fbc2ac66399b9783713

Associated Filenames msoia.exe

client.bin

client.exe

3261cbac9f0ad69dd805bfd875eb0161.exe

one68_1_1.0.apk

IPs 67.217.62[.]106

152.32.138[.]108

15.235.130[.]160

118.194.249[.]38

51.79.218[.]159

37.230.62[.]73

Domains gsoonmann[.]site

gmnormails[.]site

gmoonsom[.]site

nasanecesoi[.]site

gmoocsoom[.]site

gmcomamz[.]site

namerowem[.]site

gmoosomnoem[.]site

mncomgom[.]site

ggnmcomas[.]site

updatetiker[.]net

updatetiker[.]site

gomncomow[.]site

gooczmmnc[.]site

gnmoommle[.]space

one68[.]top

remote[.]henh247[.]net

remote[.]henho247[.]net

VII. Recommendations

Exercise Good Cyber Hygiene – The easiest, most effective way to prevent system compromise via Remote Access Trojans like SparkRAT is to simply practice good cyber hygiene. This includes not opening unknown files, being suspicious of email attachments from untrusted sources, avoiding downloading software from unofficial websites, and regularly updating operating systems.

Isolated Virus Scans – Performing a malware detection scan (via crowdsourced tools like VirusTotal or antivirus software like Microsoft Defender’s custom scan option) on an untrusted file before executing it can be an easy way to verify its legitimacy. Fortunately, most AV solutions are privy to common SparkRAT indicators and will prevent infected files from executing. However, custom malware leveraging the tool may go undetected. If further analysis is required, it is advised to run any suspected file within a sandbox environment to examine its behavior.

Update Virus Signatures – Ensuring that endpoint solutions and antivirus software are up to date with the latest virus signatures is crucial for detecting and quarantining known variations of SparkRAT malware. Signature databases used by AV software are typically populated with new signatures when applying the latest security patches. For this reason, it is recommended to frequently update (daily) or configure automatic system/application updates.

Active Network Monitoring – A system infected with SparkRAT malware establishes a connection to its C2 server via WebSocket, a web-based application protocol that enables full-duplex communication between client and server [8]. Though sometimes used by legitimate software, such as instant messengers and multiplayer games, the use of this protocol over port 8000 (the default port for SparkRAT agents) could be a strong indicator of SparkRAT activity. To detect this traffic, network monitoring and deep packet inspection tools can be deployed to look for abnormal connections over port 8000, WebSocket handshakes by unknown applications, and JSON error messages indicative of SparkRAT C2.

Stay Informed – As SparkRAT gains traction, it is likely to be featured in future malware campaigns. Thankfully, threat hunters and intelligence agencies are vigilantly discovering and sharing IOCs linked to the tool. Engaging with threat intel networks and staying aware of new SparkRAT trends will allow for better preparation of systems and aid in detection efforts of emerging threats.

VIII. References

[1] Arctic Wolf. (November 3, 2023). Exploitation of CVE-2023-46604 in Apache ActiveMQ Leads to TellYouThePass Ransomware. https://arcticwolf.com/resources/blog/tellmethetruth-exploitation-of-cve-2023-46604-leading-to-ransomware/

[2] Bittner, D. (Jan 29, 2025). Cats and RATS are all the rage. https://thecyberwire.com/podcasts/daily-podcast/2234/transcript

[3] Broadcom (January 31, 2025). SparkRAT – a cross-platform modular malware. https://www.broadcom.com/support/security-center/protection-bulletin/sparkrat-a-cross-platform-modular-malware

[4] ClearSky (November 13, 2024). CVE-2024-43451: A New Zero-Day Vulnerability Exploited in the wild. https://www.clearskysec.com/0d-vulnerability-exploited-in-the_wild/

[5] Fernández, G. (Nov 27, 2024). SparkRAT: Server Detection, macOS Activity, and Malicious Connections. https://x.com/1ZRR4H/status/1861667506328334589/

[6] Fortinet. (February 13, 2024). Threat Coverage: How FortiEDR protects against SparkRAT activity. https://community.fortinet.com/t5/FortiEDR/Threat-Coverage-How-FortiEDR-protects-against-SparkRAT-activity/ta-p/299271

[7] Hunt.io. (Jan 28, 2025). SparkRAT: Server Detection, macOS Activity, and Malicious Connections. https://hunt.io/blog/sparkrat-server-detection-macos-activity-and-malicious-connections

[8] IETF. (Dec 2011). The WebSocket Protocol. https://datatracker.ietf.org/doc/html/rfc6455

[9] Mishra, A. (Jan 29, 2025). Hackers Attacking Windows, macOS, and Linux systems With SparkRAT. https://gbhackers.com/hackers-attacking-windows-macos-and-linux-systems/

[10] SentinelLabs. (Jan 24, 2023) DragonSpark | Attacks Evade Detection with SparkRAT and Golang Source Code Interpretation. https://www.sentinelone.com/labs/dragonspark-attacks-evade-detection-with-sparkrat-and-golang-source-code-interpretation/

[11] XZB-1248. (Mar 16, 2022). SparkRAT GitHub Repository. https://github.com/XZB-1248/Spark

Additional Resources

[12] Open Threat Exchange. “SparkRAT”. https://otx.alienvault.com/browse/global/pulses?q=SparkRAT&include_inactive=0&sort=-modified&page=1&limit=10&indicatorsSearch=SparkRAT

[13] Malpedia. “SparkRAT”. https://malpedia.caad.fkie.fraunhofer.de/details/win.spark_rat

[14] ThreatFox. SparkRAT IOCs. https://threatfox.abuse.ch/browse/malware/win.spark_rat/

[15] Hybrid Analysis. client.bin Sandbox Report. https://www.hybrid-analysis.com/sample/cd313c9b706c2ba9f50d338305c456ad3392572efe387a83093b09d2cb6f1b56

[16] VirusTotal. client.bin Scan. https://www.virustotal.com/gui/file/cd313c9b706c2ba9f50d338305c456ad3392572efe387a83093b09d2cb6f1b56

Threat Advisory created by The Cyber Florida Security Operations Center.

Contributing Security Analyst(s): Isaac Ward

SparkRAT: A Multi-Platform Remote Access Tool2025-03-04T14:33:16-05:00